


Ukrainian Websites Targeted by ClickFix Campaign
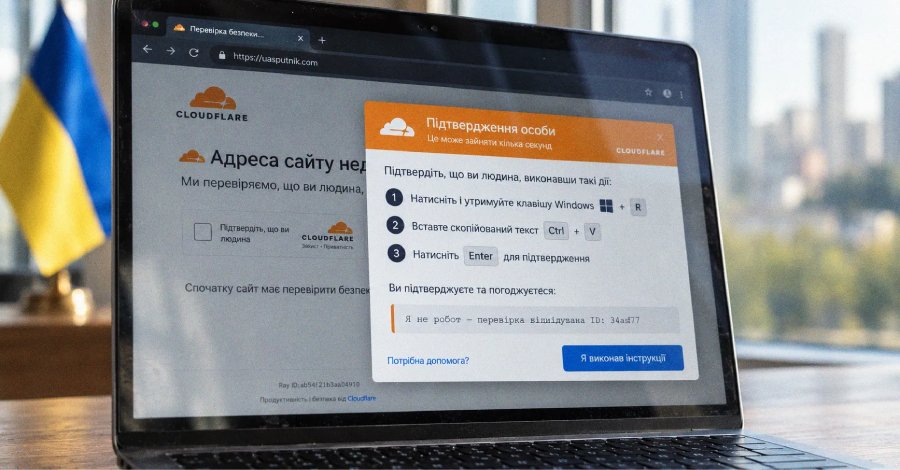
Recent cyberattacks on Ukrainian websites are utilizing a ClickFix campaign to deceive visitors with fake Cloudflare verification pages. These pages are designed to trick users into downloading an unknown malware named Psychedelic, which acts as an information thief. The attackers have compromised legitimate Ukrainian business sites to host the fake pages. When a visitor interacts with the page, a Windows Installer command is copied to the clipboard. Users are then prompted to paste this command into their command prompt, leading to an unwanted installation of the malware.
The Psychedelic malware is currently undocumented and poses a serious threat to cybersecurity. Experts warn that the malware is capable of stealing sensitive information from the affected systems, potentially resulting in significant financial and reputational damage to the impacted companies. Security researchers have noted that the attacks are specifically targeting businesses in Ukraine, indicating a possible political motivation. The use of fake Cloudflare pages is a common tactic to gain user trust and entice them into installing malware. Cloudflare itself has responded to the incidents, emphasizing that they are actively working to identify and remove the affected pages.
The company has also recommended that users exercise caution when clicking on links that lead to verification pages, especially if they do not originate directly from the Cloudflare website. The security situation in Ukraine remains tense, particularly in the context of ongoing geopolitical conflicts. Cyberattacks are a frequent means of exerting pressure on the Ukrainian government and businesses. The current campaign could be part of a larger strategy aimed at undermining the stability of the country. IT security experts advise companies to regularly review their systems and ensure that all security updates are installed.
Implementing multi-factor authentication processes can also help minimize the risk of a successful attack. The exact number of affected websites is currently unknown; however, security researchers have already identified several dozen compromised sites. The attacks appear to be spreading across various industries, underscoring the need for a comprehensive security strategy. Investigations into the background of the attacks are ongoing. Security analysts are working to identify the origins of the Psychedelic malware and establish possible connections to known hacker groups.
The discovery of this malware could have far-reaching implications for cyber defense in the region. The vulnerability exploited by these attacks could also affect other countries that utilize similar security infrastructures. The international community is urged to collaborate in combating the threat posed by such cyberattacks and to enhance internet security. The incidents highlight the growing importance of cybersecurity in today's digital world. Companies must take proactive measures to defend against such threats and protect their data.
Initial reports of the ClickFix campaign were published last week, and security authorities in Ukraine have already taken steps to warn affected companies and offer support. The Psychedelic malware could be capable of stealing a variety of data, including passwords, financial information, and personal data. The exact functioning of the malware is currently being analyzed by security experts. The Ukrainian government has announced that it will strengthen its cyber defense to better address such threats in the future. A comprehensive program to improve cybersecurity is set to be implemented in the coming months.
The vulnerability exploited by these attacks could also affect other countries that utilize similar security infrastructures.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!