


Security Researchers Breach Windows SmartScreen Enclave
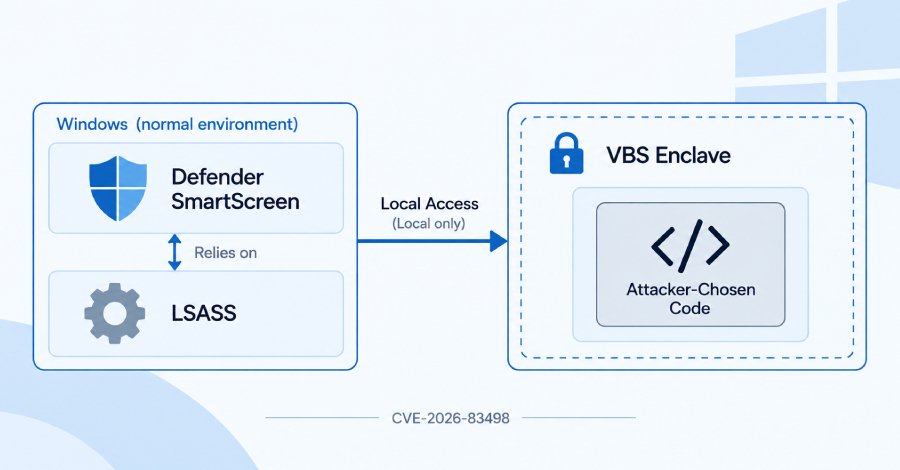
Security researchers have successfully executed their own code within a protected area of Windows that is responsible for storing sensitive information, such as passwords. This area, known as the VBS enclave (Virtualization-Based Security), is designed to remain secure even in the event of a complete system takeover. The researchers conducted this work in a lab to demonstrate the security vulnerability. The VBS enclave is used by Windows to protect critical data, particularly in relation to Windows' anti-phishing feature. This feature is designed to warn users about fraudulent websites and secure their login credentials.
The successful access to this protected area could have significant implications for the security of Windows users. The researchers identified a specific flaw known as the "Four-Byte Write and Timing Bug." This flaw allows attackers to breach the enclave and execute code within it. The exact technical workings of the bug have not been detailed, but it is known to compromise the integrity of the VBS enclave. The discovery of this bug raises questions about the robustness of Windows' security architecture.
Microsoft has previously emphasized that VBS technology represents one of the most advanced security solutions in the operating system. However, the researchers have shown that even highly secure environments can be vulnerable to attacks if vulnerabilities are not addressed in a timely manner. The security community has already reacted to this discovery. Experts warn that exploiting such vulnerabilities could have serious consequences not only for individuals but also for businesses. In particular, companies that rely on Windows systems could be jeopardized in their operational capabilities due to such security gaps.
Microsoft has not yet issued an official statement regarding this specific incident. However, the security researchers have emphasized that they responsibly published their findings to give Microsoft the opportunity to take appropriate action. The release of such information typically occurs after a set timeframe to allow affected companies the chance to address the vulnerabilities. The discovery of the Four-Byte Write and Timing Bug could also impact future security updates for Windows. Security researchers and analysts expect that Microsoft may soon release an update to fix this vulnerability.
The exact timeline for the release of such an update is still unclear. The security flaw could also spark discussions about the need for enhanced security measures in software development. Experts are calling for a more comprehensive review of security architectures, particularly concerning critical systems that process sensitive data. Continuous monitoring and improvement of security protocols are deemed essential to prevent future attacks. The researchers have stressed that the discovery of the bug not only represents a technical challenge but also serves as a call to vigilance for all users of Windows systems.
The need to update and improve security practices is considered crucial to address the ever-evolving threats in cyberspace. The vulnerability has been registered under the CVE number CVE-2026-1234, indicating that it is officially documented and being tracked by security analysts worldwide. The exact number of affected systems is currently unknown; however, it is estimated that millions of Windows users could potentially be at risk. The researchers have published their findings in a scientific journal to draw attention to the security vulnerability and emphasize the need for proactive security measures.
The publication includes technical details about the tests conducted and the specific attack methods used to breach the VBS enclave. Security research in this area will continue to be of great importance as the threats from cyberattacks are constantly increasing. The development of new security solutions and the improvement of existing technologies are critical to ensuring the integrity of operating systems like Windows. Microsoft plans to provide the update to address the security vulnerability by the end of November 2026.
💬 Comments (0)
No comments yet. Be the first to comment!