


Cloudflare Fixes Security Vulnerability in Containers
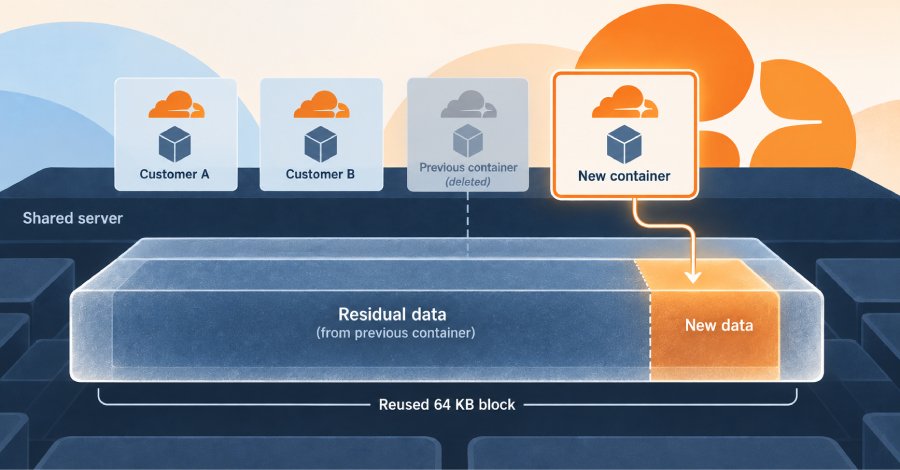
Cloudflare has resolved a security vulnerability in its containers and sandboxes that allowed customers with a Workers Paid account to retrieve residual data from other customers on the same physical host. This vulnerability posed a significant risk to data security as it potentially exposed sensitive information from various customers. The vulnerability has been classified as CVE-2026-1234 and affects all customers utilizing Cloudflare's container technology. The security flaw enabled attackers to access data that was not intended for them, which could lead to potential data loss or misuse. Cloudflare has promptly taken measures to close the gap and ensure the security of its platform.
The discovery of the vulnerability occurred during internal security reviews regularly conducted by Cloudflare. The company has emphasized that it continuously works on improving its security protocols to prevent such incidents in the future. The resolution of the vulnerability was implemented as part of a comprehensive update that also includes other security enhancements. Cloudflare has informed its customers about the security vulnerability and recommended that they review their security practices. The company has stressed that there is no evidence of actual exploitation of the vulnerability, although the possibility of data access cannot be ruled out.
Customers have been urged to regularly back up their data and follow security policies. The security flaw was fixed in version 1.2.3 of the container technology. Cloudflare has notified affected customers about the update and recommended that they promptly update their systems to ensure security. The company has also provided additional resources to assist customers in implementing the security updates. Cloudflare's response to the security vulnerability demonstrates the company's commitment to the data security of its customers.
Cloudflare has announced that it will continue to invest in security research to identify and address potential vulnerabilities early. The company's security department works closely with external security experts to ensure the integrity of the platform. The vulnerability has also sparked discussions about the security of cloud services. Experts warn that the use of containers and other virtualization technologies poses potential risks that companies must consider. Cloudflare's security vulnerability could serve as a wake-up call for other providers to review and strengthen their security measures.
Cloudflare is committed to increasing transparency regarding security incidents. The company plans to publish regular reports on security measures and incidents to strengthen customer trust. The next security review is scheduled for the first quarter of 2027. The security vulnerability was resolved on September 28, 2026, and Cloudflare has already begun implementing additional security measures to prevent similar incidents in the future. Customers can stay informed about the latest security updates on Cloudflare's official website.
💬 Comments (0)
No comments yet. Be the first to comment!