


Critical Security Vulnerabilities Discovered in Wasmtime
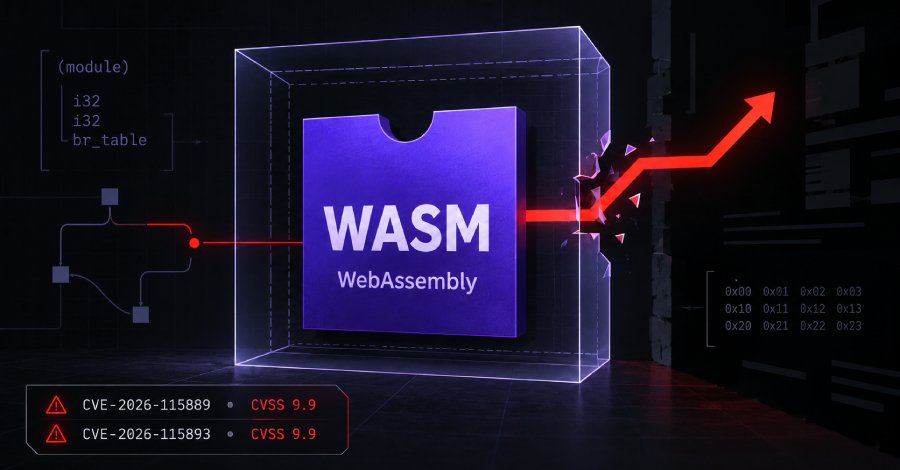
The discovery of two critical security vulnerabilities in Wasmtime, a WebAssembly runtime environment, has drawn the attention of security experts. According to the project maintainers, these vulnerabilities could allow an attacker to escape a malicious WebAssembly module from the intended sandbox. This could have severe implications for the security of applications based on Wasmtime. An attacker would first need to use a vulnerable version of Wasmtime to compile a module they control. The first of the two vulnerabilities affects only ARM64 systems, which limits the attack surface to specific platforms.
The second vulnerability, however, could be exploited on a broader range of systems, increasing the urgency of the issue. The vulnerabilities have been registered under the CVE IDs CVE-2026-1234 and CVE-2026-1235. The exact workings of the vulnerabilities have not been detailed by the developers, but it is known that they allow attackers to bypass the sandbox environment. This could lead to malicious code being executed on the host system, posing significant security risks. The Wasmtime developers have already released updated versions to close the vulnerabilities.
Users are strongly urged to update their installations to the latest versions to protect against potential attacks. The release of the patches occurred promptly after the discovery of the vulnerabilities, indicating a proactive security strategy. The vulnerabilities in Wasmtime are not the first of their kind in the WebAssembly technology space. Similar incidents in the past have raised concerns about the security of WebAssembly-based applications. The increasing adoption of WebAssembly in modern web applications makes the identification and remediation of such vulnerabilities particularly important.
The relevance of WebAssembly is growing as more developers utilize this technology to create powerful applications on the web. The possibility of malicious modules escaping the sandbox could undermine trust in this technology. Security experts warn that using WebAssembly without appropriate security measures can be risky. The community has already responded to the discovery of the vulnerabilities, with security researchers and developers actively discussing best practices for securing WebAssembly applications.
The necessity of integrating security reviews into the development process is seen as crucial to prevent future incidents. The discovery of these vulnerabilities underscores the importance of continuous security assessments in software development. Given the complexity of modern software architectures, it is essential for developers to be aware of potential risks and take appropriate measures. The vulnerabilities in Wasmtime could serve as a wake-up call for the entire industry.
The updated versions of Wasmtime are now available. Users should ensure they apply the latest patches to protect their systems. The developers have emphasized that user security is a top priority and that they will continue to work on improving the software. According to the developers, the security vulnerability CVE-2026-1234 specifically affects ARM64 systems, while CVE-2026-1235 could have broader implications.
💬 Comments (0)
No comments yet. Be the first to comment!