


Google Fixes Security Vulnerability in Pixel Modem
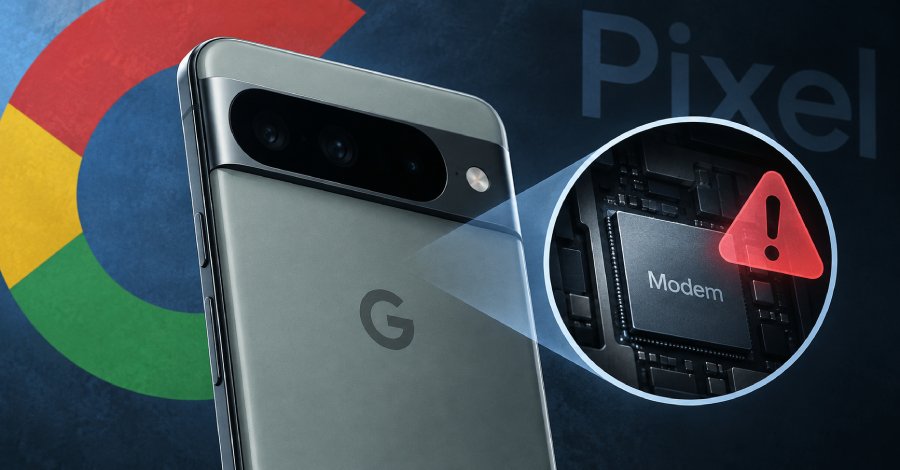
Google has disclosed a high-severity security vulnerability in its Pixel Cellular Modem that is already being exploited in the wild. The flaw, identified as CVE-2026-58704, has a CVSS score of 8.0 and pertains to privilege escalation. According to the description in the NIST National Vulnerability Database, it involves a potential permission bypass due to a logical error in the code. The vulnerability allows attackers to potentially gain unauthorized permissions, leading to an increased risk for the affected devices. Google has already taken steps to address the vulnerability and provide an update.
Users of the affected Pixel devices are strongly urged to install the update promptly to protect their devices. The exact number of affected devices has not been disclosed by Google. However, experts estimate that a significant number of users worldwide could be impacted, as the Pixel series is widely used in many countries. The vulnerability could pose a serious risk, particularly for businesses and organizations that rely on mobile communication. The discovery of the flaw comes at a time when cyberattacks on mobile devices are on the rise.
Security researchers warn that attackers are increasingly conducting targeted attacks on specific vulnerabilities in widely used software and hardware. The fact that this vulnerability is already being exploited underscores the urgency of quickly implementing security updates. Google has previously released several security updates for its Pixel devices to address similar vulnerabilities. The swift response to this new threat demonstrates the company's commitment to the safety of its users. Security updates are typically available through the device settings and can be easily downloaded and installed.
The vulnerability was discovered last week, and Google has promptly responded to analyze and fix the flaw. The release of the update will occur in several phases to ensure that all affected users are protected as quickly as possible. Google recommends enabling the automatic update feature to ensure that all security updates are installed in a timely manner. The CVE-2026-58704 vulnerability is not the first of its kind discovered in mobile devices. Similar issues have been identified in the past with other manufacturers, highlighting the need for regular security reviews and updates.
Users should be aware that the security of their devices depends on the currency of the installed software. The security gap has been independently identified by several security researchers, emphasizing the importance of collaboration within the security community. By sharing information and responding quickly to newly discovered vulnerabilities, companies and users can be better protected. Google has already announced that it will continue to invest in improving the security of its products.
The release of the update to address the vulnerability is expected to occur in the coming days for all affected Pixel devices. Users should regularly check for updates and ensure that their devices are up to date to minimize potential security risks. According to Google, the update for the Pixel devices will be rolled out by no later than September 30, 2026.
💬 Comments (0)
No comments yet. Be the first to comment!