


N-able Warns of Vulnerabilities in N-central
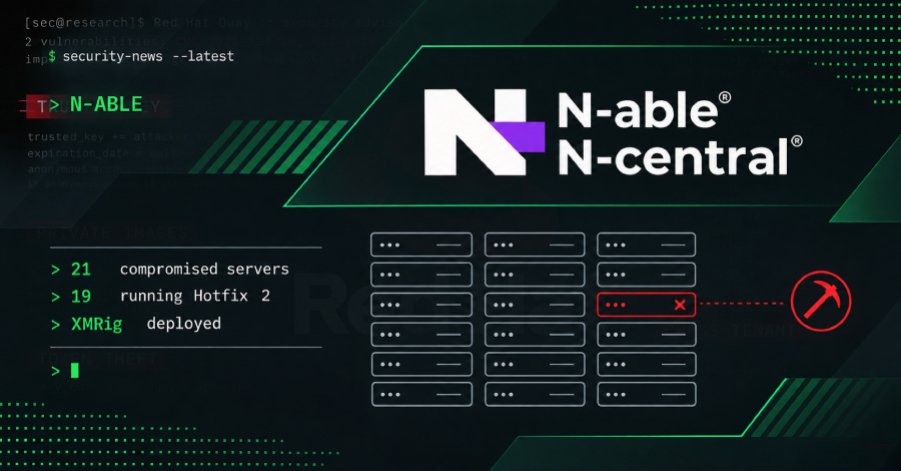
N-able announced on Thursday that a new set of vulnerabilities, tracked as 4EverAble2Shell and Agent2Shell, has been discovered. These vulnerabilities affect a total of 21 servers, including 19 that are running Hotfix 2. In response to the public disclosure of these security issues, the company has taken additional precautions. In an update, N-able stated that certain features and integrations of N-central will be restricted. These measures may impact some functionalities; however, they are necessary to ensure the security of the systems while the vulnerabilities are being addressed.
The exact details regarding the affected features have not been disclosed. The vulnerabilities allow attackers to potentially access and compromise the affected servers. N-able has emphasized that customer security is the highest priority and that the company is actively working to resolve the issues. The affected servers are part of a larger network utilized by various companies. The vulnerabilities were discovered by security experts and promptly reported to N-able.
The company has assembled a team of professionals to analyze the vulnerabilities and develop appropriate remediation measures. The exact number of affected customers has not been disclosed. To minimize the impact of the vulnerabilities, N-able has recommended that all customers promptly review their systems and ensure that they have the latest security updates installed. The company plans to provide further information in the coming days to assist customers in securing their systems. The vulnerabilities 4EverAble2Shell and Agent2Shell are part of a growing list of vulnerabilities discovered in various software solutions in recent months.
Experts warn that such security issues are becoming increasingly common and should prompt companies to review and update their security protocols. N-able has committed to regularly informing affected customers about the progress of the remediation of the vulnerabilities. The company plans to provide a comprehensive update in the coming weeks detailing the measures taken and the next steps. The vulnerabilities have already been classified as a serious threat in the industry. Experts advise companies to take proactive measures to protect their systems and prevent potential attacks.
A detailed technical analysis of the vulnerabilities is currently underway to better assess the risks. The discovery of these vulnerabilities comes at a time when cyberattacks on companies worldwide are increasing. According to a recent study, 70% of companies have reported an increase in cyberattacks over the past 12 months. N-able has stressed that the security of customer systems and data is of utmost priority and that all necessary steps will be taken to protect them. The vulnerabilities 4EverAble2Shell and Agent2Shell are another example of the challenges companies face in the field of cybersecurity.
N-able has announced that it will continue to work closely with security experts to ensure the integrity of its products and to avoid future security issues. The affected servers are currently being monitored to ensure that no unauthorized access occurs. N-able has urged customers to report any suspicious activities immediately to enable a swift response. The vulnerabilities were publicly disclosed on November 15, 2026.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!