


GitLab Addresses Critical Security Vulnerability in AI Gateway
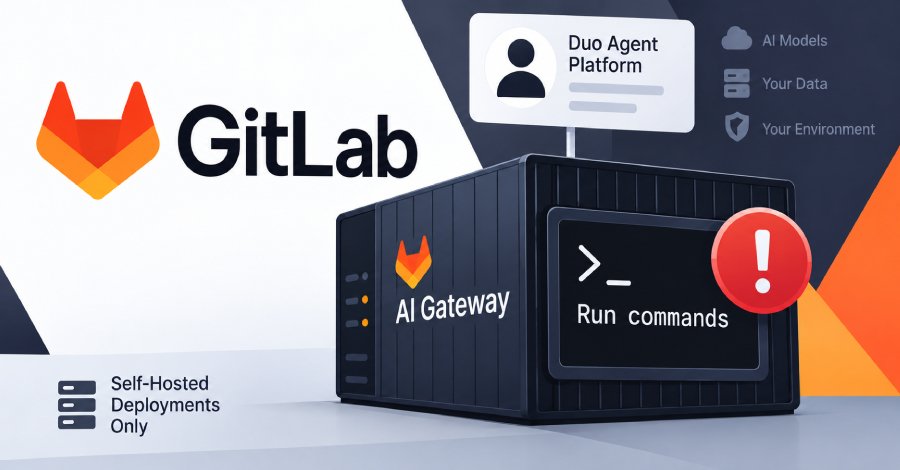
GitLab has identified a critical security vulnerability in the AI Gateway that could allow a logged-in user with access to the Duo Agent Platform to execute commands on the gateway. This vulnerability only affects organizations that host their own gateways. According to an official statement from GitLab, affected users are urged to take immediate action to protect their systems. The vulnerability has been addressed in versions 19.2.4, 19.3.2, and 19.4.1 of the gateway. GitLab recommends that all users upgrade to these versions to minimize the risk of an attack.
The exact CVE number for this security vulnerability has not yet been released. The AI Gateway serves as an interface between a GitLab instance and various AI models. This functionality is critical for many companies as it enables access to AI-powered tools and services. The discovery of this vulnerability could therefore have far-reaching implications for the security of self-hosted GitLab instances. The vulnerability was discovered internally by GitLab and promptly addressed.
The company has emphasized that the security of its users is a top priority and that proactive measures are being taken to identify and resolve such vulnerabilities. The swift response to this discovery demonstrates GitLab's commitment to the security of its products. The affected versions of the AI Gateway are typically used in companies that rely on customized solutions. These organizations must ensure that their systems are up to date to prevent potential attacks. Upgrading to the latest versions is a crucial step in ensuring the integrity of the systems.
The vulnerability could allow attackers to execute unauthorized commands, potentially leading to a complete compromise of the system. This could result not only in data loss but also in significant reputational damage for affected companies. The exact nature of the commands that could be executed has not been specified by GitLab. IT security experts advise regularly reviewing systems and ensuring that all security updates are installed promptly. Implementing security policies and conducting regular employee training are also important measures to enhance security.
Companies should also consider conducting external security audits to identify potential vulnerabilities. The discovery of this vulnerability comes at a time when the use of AI technologies in businesses is rapidly increasing. Integrating AI into existing systems brings not only benefits but also new challenges regarding security. Companies must be aware of these risks and take appropriate measures. GitLab has announced that further information regarding the vulnerability and recommended actions will be released in the coming days.
The community is urged to stay vigilant and consult GitLab's official channels for up-to-date information. The vulnerability is classified as critical, meaning immediate action is required. The security vulnerability in GitLab's AI Gateway is an example of the challenges associated with increasing digitization and the use of AI technologies. Companies must continuously adapt and rethink their security strategies to address new threats. Upgrading to the latest versions of the gateway should be completed by October 15, 2026, to minimize security risks.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!