


Critical Security Vulnerability Discovered in FortiMail
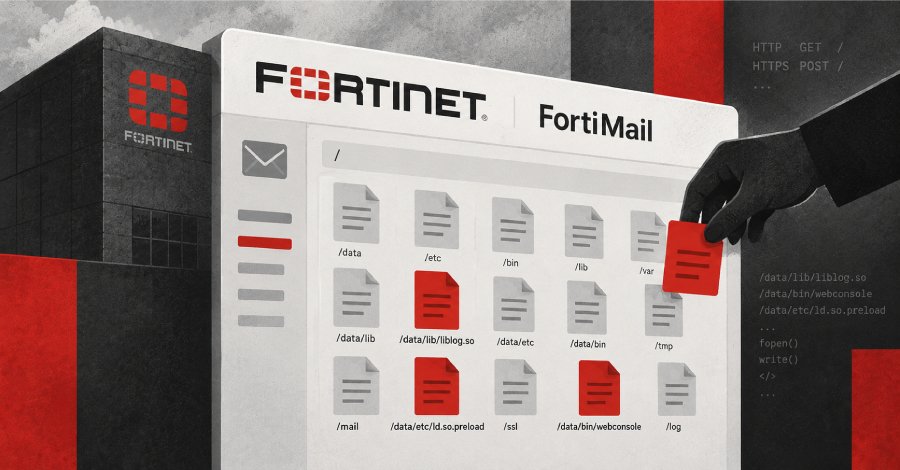
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a critical security vulnerability in Fortinet FortiMail to its Known Exploited Vulnerabilities (KEV) catalog on Thursday. The vulnerability, classified as CVE-2026-104286, has a CVSS score of 9.8 and allows unauthorized attackers to write arbitrary files to the underlying system. Reports indicate that the vulnerability is actively being exploited, increasing the urgency for security updates. CISA has urged organizations to take immediate action to protect their systems.
The vulnerability results from improper input validation, allowing attackers to inject malicious data. Fortinet has already released a security update to address the vulnerability. The affected versions of FortiMail are not specified; however, it is recommended that all systems be updated promptly. CISA has also provided detailed guidance on how administrators can identify and remediate the vulnerability. The discovery of this vulnerability comes at a time when cyberattacks on businesses and institutions worldwide are on the rise.
According to a report by Cybersecurity Ventures, a business becomes a victim of a ransomware attack every 11 seconds. The need to strengthen security measures is further underscored by such incidents. Fortinet has previously reported several vulnerabilities in its products. However, the current vulnerability is particularly concerning as it allows attackers to access critical system resources without authentication. This could lead to significant data loss and system outages.
CISA recommends that companies review their security policies and ensure that all systems are up to date. Implementing Intrusion Detection Systems (IDS) and conducting regular security audits could also help detect potential attacks early. The CVE-2026-104286 vulnerability exemplifies the growing challenges businesses face in cybersecurity. Experts warn that the complexity of modern IT infrastructures makes it easier for attackers to exploit vulnerabilities. CISA has emphasized that proactive measures are essential to ensure the security of IT systems.
The vulnerability has been independently identified by several security researchers, highlighting the urgency of the situation. Fortinet is committed to continuously improving the security of its products and has already taken steps to protect the affected systems. CISA will continue to monitor the situation and provide further information as necessary. The release of the security update by Fortinet comes at a critical time, as many companies need to upgrade their IT infrastructure to meet the latest standards. CISA has stressed that the rapid implementation of security updates is crucial to minimizing the risk of cyberattacks.
The vulnerability affects not only FortiMail but could also impact other Fortinet products that use similar security architectures. Therefore, companies should review all relevant systems and ensure they are protected against this type of attack. CISA has urged the security community to remain vigilant and share information about potential attacks. Collaboration between businesses and security agencies is considered essential to strengthen cyber defense and prevent future attacks. The vulnerability was added to the KEV catalog on October 3, 2026, underscoring the urgency of the situation. Companies are urged to act promptly to secure their systems.
💬 Comments (0)
No comments yet. Be the first to comment!