


Gigabud Trojan Uses Android Work Profiles for Concealment
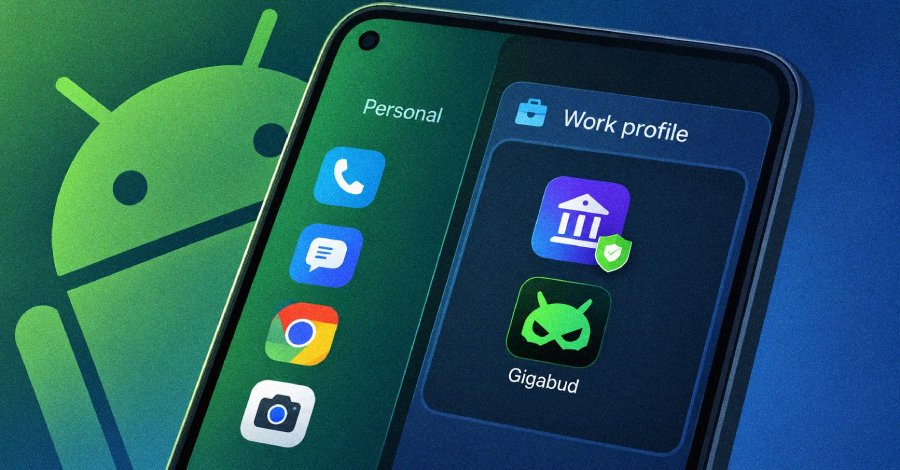
The Gigabud banking Trojan has developed a new method to hide from security checks of banking apps. According to a report by the security firm Group-IB, published on September 9, 2026, the Trojan installs a second Android app that creates a work profile on the infected device. This work profile is a separate area typically reserved for corporate applications, separating the data contained within from the user's personal data. The Trojan's functionality allows for a manipulated version of a banking app to be placed within the work profile.
This technique makes it more difficult for security software to detect the malicious app, as it operates in an area that most users and security solutions consider safe. The use of work profiles is widespread in Android to protect corporate data and separate the use of personal and business applications. Group-IB's security researchers have found that this method is particularly effective, as many users do not expect their banking apps to be compromised within a work profile. The installation of the Trojan typically occurs through fake applications or phishing attacks aimed at tricking users into installing the malicious software. Another concerning aspect is that the Gigabud Trojan not only targets Android devices but is also capable of stealing sensitive information such as login credentials and banking information.
The malware can present itself in various forms, further complicating detection by security solutions. Researchers warn that the threat from such Trojans could increase in the coming months, as cybercriminals continuously develop new techniques. The security firm has recommended that users regularly check their devices for suspicious activities and only install applications from trusted sources. Additionally, they should ensure that their security software is always up to date to protect against such threats. The use of two-factor authentication for banking applications is also highlighted as an important measure.
The discovery of the Gigabud Trojan is part of a larger trend where cybercriminals increasingly use complex methods to disguise their attacks. Security researchers have observed a rise in malware attacks specifically aimed at stealing banking data in recent months. These attacks are often well-planned and utilize social engineering techniques to gain users' trust. The group of security researchers investigating the Gigabud Trojan plans to publish their findings in a comprehensive study that will include detailed information about the operation and spread of this malware. This study aims to raise awareness of the threats posed by banking Trojans and develop effective countermeasures.
The security situation in the mobile application sector remains tense, as more users rely on digital banking services. According to a recent survey, over 70% of smartphone users in Germany use banking apps, making them an attractive target for cybercriminals. Experts consider the need to strengthen security measures urgent. Group-IB has already collaborated with various banks and technology providers to minimize the impact of the Gigabud Trojan. This collaboration aims to develop security solutions capable of early detection and defense against such threats.
Initial results from these collaborations are expected to be published by the end of 2026. The discovery of the Gigabud Trojan and its new concealment methods highlights the ongoing challenge faced by security researchers and users. The development of malware that hides within legitimate applications requires continuous adaptation of security strategies. Experts emphasize that raising user awareness of such threats is crucial to ensuring security in digital banking. The vulnerability exploited by the Gigabud Trojan could potentially affect millions of users if no appropriate measures are taken. Group-IB researchers estimate that the malware is already active in several countries and spreading rapidly. The exact number of affected devices is currently unknown; however, a comprehensive investigation is underway to determine the extent of the threat.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!