


WorkOS Suffers Data Breach Due to ARTEX AI Attack
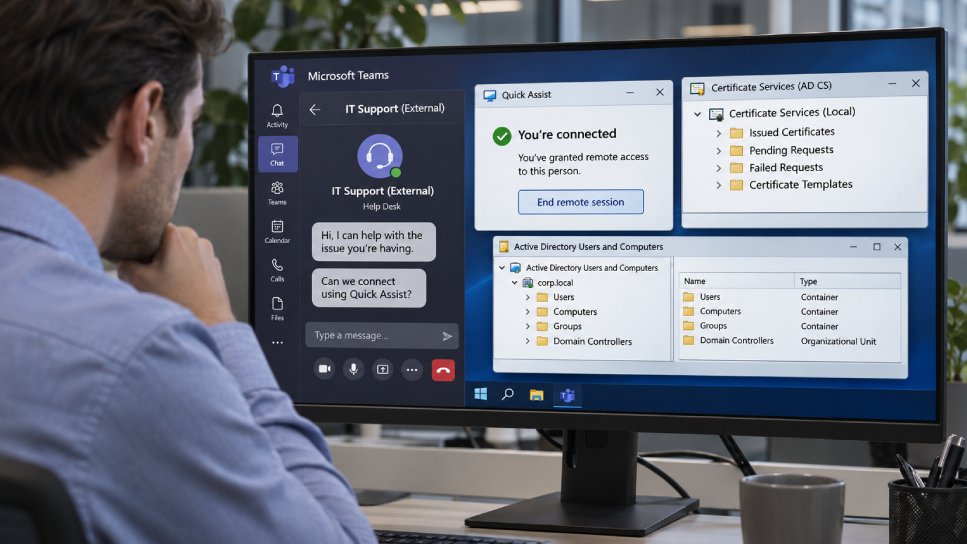
WorkOS has announced a data incident in which an attacker accessed internal sales applications through the AI platform ARTEX AI. The incident resulted in the disclosure of business contact information and summaries of customer communications. The security vulnerability was discovered on November 1, 2026, and was promptly investigated. Initial findings indicate that the attacker was able to penetrate the system through an authentication vulnerability.
The exact method used to bypass security measures is currently under thorough investigation. WorkOS has promptly informed affected customers and initiated damage control measures. The compromised data includes names, email addresses, and phone numbers of business partners. WorkOS emphasized that no sensitive financial data or passwords were compromised. Nevertheless, the incident could undermine customer trust in the platform.
In response to the incident, WorkOS has reviewed and strengthened its security protocols. The company plans to implement additional security measures to prevent future attacks, including the introduction of multi-factor authentication processes and regular security audits. The ARTEX AI platform, which was used for the attack, is known for its ability to analyze large datasets and recognize patterns. Experts warn that such AI-powered tools can be used for both legitimate and malicious purposes.
The use of AI in cyberattacks may increase in the future, highlighting the need to optimize security measures. WorkOS is committed to maintaining transparency with its customers and will provide regular updates on the progress of the investigation. The company has also engaged external security experts to determine the causes of the incident and strengthen its security infrastructure. Reactions to the incident are mixed, with some customers expressing concerns about data security while others praise WorkOS's proactive communication.
Industry analysts emphasize that companies in today’s digital landscape must remain particularly vigilant to address cyber threats. The security vulnerability that led to this incident could also impact other companies using similar technologies. Experts advise regularly reviewing and adjusting security policies to address the ever-evolving threats. The exact number of affected customers has not yet been disclosed by WorkOS.
WorkOS plans to release the results of the investigation by the end of November 2026. The company has already taken steps to improve its security posture and regain customer trust. “We take this incident very seriously and are working closely with our security teams to clarify the situation,” a company spokesperson stated. “The security of our customers is our top priority.”
💬 Comments (0)
No comments yet. Be the first to comment!