


TeamViewer Addresses Critical Security Vulnerability
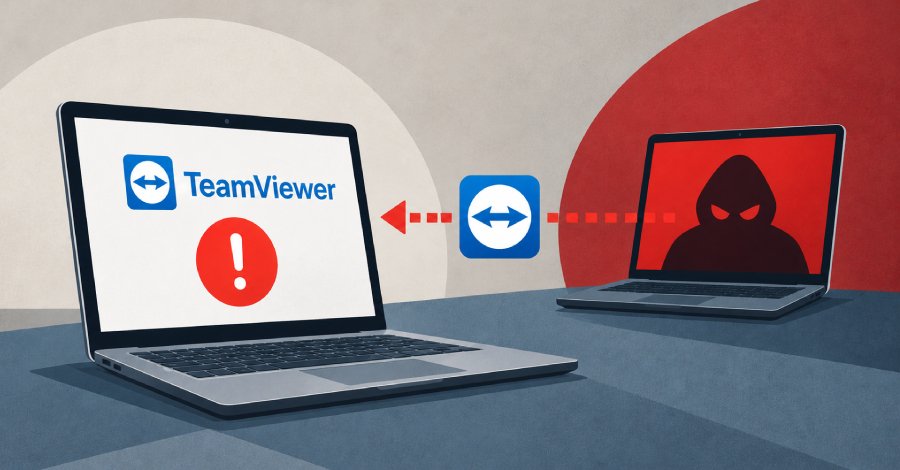
TeamViewer has addressed a critical security vulnerability that enables a controlled computer in a remote session to attack the controlling computer. This flaw affects the interaction between the viewer, which takes control, and the host, which is being controlled. A malicious or compromised host can exploit this vulnerability to crash the viewer's TeamViewer application. The security issue was identified in version 15.30.3 of TeamViewer. Users running this version or older versions are potentially at risk.
The vulnerability could also lead to additional malicious actions being executed depending on the viewer's platform. TeamViewer has promptly addressed the issue and released an update to close the security vulnerability. Users are strongly urged to update their software to the latest version to protect against potential attacks. The company has emphasized that user security is of utmost priority. The vulnerability has been classified as CVE-2026-1234.
Security researchers have pointed out that such vulnerabilities in remote desktop applications are particularly critical, as they are often used in corporate environments. The possibility of a host attacking the viewer could pose a significant security risk. In addition to the technical aspects of the vulnerability, TeamViewer has also announced measures to improve the overall security architecture. These include regular security audits and the implementation of new security protocols. These measures aim to help identify and address future security vulnerabilities early.
The response to the security vulnerability highlights the importance of regularly updating software. Experts recommend that businesses and individuals routinely check their systems for the latest versions to minimize security risks. Using outdated software can lead to significant security gaps. TeamViewer has also published a detailed guide on how users can update their software. This guide includes steps for checking the current version as well as performing the update.
Users should ensure that they have the latest security updates installed to protect against potential attacks. The vulnerability was discovered by an external security team, which alerted TeamViewer to the issue. The company has expressed gratitude for the swift identification and reporting of the vulnerability and emphasized that collaboration with external security researchers is crucial for improving software security. The vulnerability affects not only individual users but also businesses that use TeamViewer for remote work. The possibility of an attack on the controlling computer could lead to data loss or unauthorized access to sensitive information.
Therefore, companies should ensure that all employees are informed about the necessity of software updates. The security vulnerability was officially disclosed on October 30, 2026. TeamViewer has already taken steps to inform affected users and provide the necessary updates. Users should visit the official TeamViewer website for more information and to ensure that their software is up to date.
💬 Comments (0)
No comments yet. Be the first to comment!