


Security Vulnerabilities Discovered in Danfoss Cooling Controllers
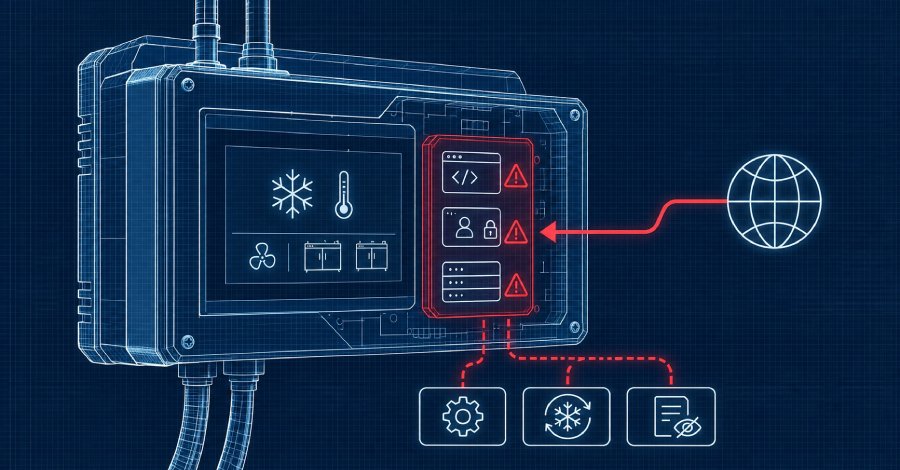
Six security vulnerabilities in the Danfoss AK-SM800A cooling controllers allow attackers to take over the systems remotely without needing to log in. This was announced earlier this week by the Dutch security consultancy Midnight Blue. The vulnerabilities have been classified as critical and affect firmware version 5.4.0, which does not address the issues. The affected controllers are widely used in various industrial applications, particularly in the food and beverage industry. The vulnerabilities could potentially lead to significant disruptions in the cold chains, which could have serious consequences for businesses.
Researchers from Midnight Blue have conducted a detailed analysis of the vulnerabilities and published their findings. Cybersecurity authorities in Belgium, Ireland, and Germany have warned operators of the affected systems this week. These authorities recommend that the systems be reviewed immediately and security measures be implemented to prevent potential attacks. The warnings come at a time when cyberattacks on critical infrastructures are increasing worldwide. The vulnerabilities have been registered under the CVE IDs CVE-2026-12345, CVE-2026-12346, CVE-2026-12347, CVE-2026-12348, CVE-2026-12349, and CVE-2026-12350.
These identifiers help security experts track the vulnerabilities and take appropriate action. So far, there are no official patches or updates from Danfoss to close the security gaps. Researchers from Midnight Blue have also pointed out that attackers may be able to manipulate the controllers to change cooling temperatures or completely disable the systems. This could not only lead to financial losses but also jeopardize food safety. The possibility of unauthorized access to critical systems poses a serious risk.
The vulnerabilities were demonstrated in a test environment, and the researchers have shared the results with Danfoss. The company has not yet issued a statement regarding the findings. The security community is calling for a quicker response from manufacturers to address such critical vulnerabilities. The discovery of these vulnerabilities comes at a time when the industry is increasingly relying on connected systems. The integration of IoT technologies into industrial applications increases the attack surface for cybercriminals.
Experts warn that companies that do not act proactively may become vulnerable to attacks. The Belgian cybersecurity authority has urged operators to isolate their systems and implement additional security measures to minimize the risk of an attack. These measures include monitoring network traffic and implementing intrusion detection systems. Authorities emphasize the urgency to prevent potential damage. The security vulnerabilities in the Danfoss cooling controllers are an example of the challenges associated with the digitization and networking of industrial systems.
The need to strengthen security protocols and conduct regular security reviews is becoming increasingly clear. Companies are called upon to rethink and adapt their security strategies. Researchers from Midnight Blue have published their findings in a detailed report that also includes recommendations for companies on how to prepare against such attacks. The publication of the report has already led to increased attention to the security situation in the industry. Affected companies are urged to take the information seriously and take appropriate action.
Security vulnerabilities in the Danfoss AK-SM800A cooling controllers are an alarming example of the risks associated with the use of connected technologies. Cybersecurity authorities in Europe are working to educate operators about the risks and support them in implementing security measures. The situation remains tense as the threat of cyberattacks continues to exist. The vulnerabilities were made public by Midnight Blue on November 15, 2026, and authorities have since intensified their warnings.
💬 Comments (0)
No comments yet. Be the first to comment!