


Malware Campaign Discovered via npm Packages
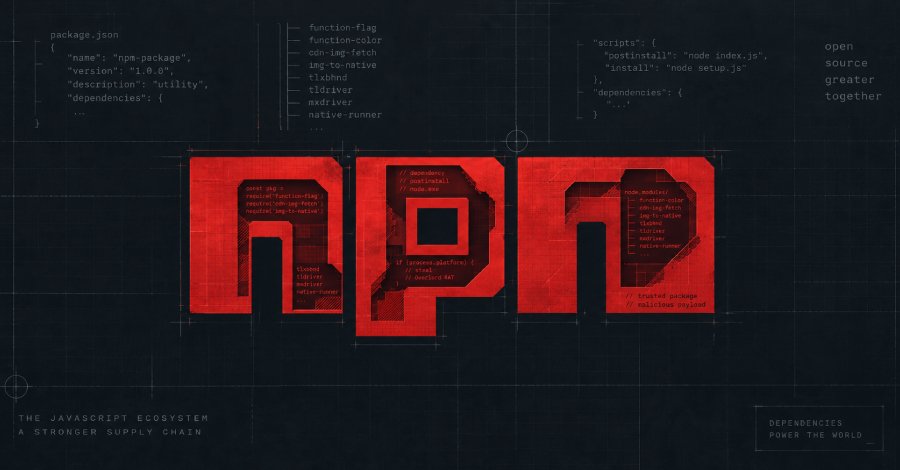
Cybersecurity researchers have released details of a prolonged malware campaign that encompasses over 40,767 downloads of malicious npm packages. This campaign, referred to as MALFEX by the companies CloudSEK and Checkmarx, aims to steal information and deploy Remote Access Trojans (RAT) on compromised systems. The investigation revealed that a single threat actor has published a total of 12 packages since August 2023. Of these packages, eight have been identified as malicious and are responsible for the distribution of RAT and information theft. The affected packages were hosted in the npm registry, a widely used platform for providing JavaScript libraries.
The malware campaign employs a variety of techniques to deceive users and install the malicious packages. These include fake descriptions and the use of popular libraries to gain developers' trust. Researchers have found that the packages are capable of stealing sensitive data such as passwords and API keys. Security analyses indicate that the malware targets not only Windows systems but also other platforms that utilize npm. This significantly expands the potential damage that the campaign can inflict.
Researchers advise developers to regularly review their dependencies and avoid suspicious packages. The affected npm packages have since been removed from the registry; however, the risk remains that already installed versions may still be active on users' systems. The researchers recommend checking all installed packages and uninstalling them if necessary to minimize the risk of an attack. The campaign has also attracted the attention of security authorities, who take the spread of such malware seriously. Experts warn that using npm packages without thorough security checks can lead to significant risks.
The incidents highlight the need to improve security practices in software development. CloudSEK and Checkmarx have published the details of the campaign in a joint report that describes the techniques and tactics of the attacker. The researchers have also provided recommendations for enhancing security in software development to prevent similar incidents in the future. The MALFEX malware campaign is an example of the growing threat posed by supply chain attacks, which have increased in recent years. Such attacks aim to exploit vulnerabilities in the software supply chain to disseminate malicious software.
Researchers emphasize the importance of security awareness and training for developers to minimize risks. The vulnerability exploited by this campaign could potentially affect thousands of developers and companies that rely on npm packages. The researchers have urged the community to remain vigilant and regularly install security updates. The complete details of the malware campaign and the affected packages are documented in the report by CloudSEK and Checkmarx. The researchers have also published a list of the affected packages that developers should review to identify potential security risks.
Security research on this campaign is ongoing to gather further information about the attacker and the techniques used. The researchers hope that by releasing this information, the developer community can be better prepared for such threats. The MALFEX malware campaign has already led to an increase in security alerts within the developer community. The researchers stress that monitoring and analyzing npm packages is crucial to preventing future attacks. The vulnerability affects a variety of systems that use npm and could potentially impact hundreds of thousands of users worldwide.
💬 Comments (0)
No comments yet. Be the first to comment!