


GitHub Actions Compromised Again
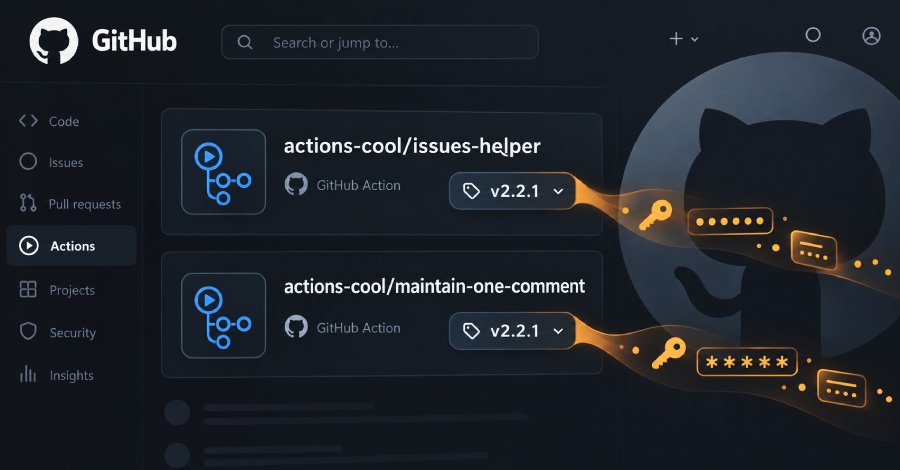
The GitHub Actions actions-cool/issues-helper and actions-cool/maintain-one-comment were disabled again after they went back online last week. These measures follow a compromise that occurred in May 2026 during the Mini Shai-Hulud campaign. The affected repositories were inaccessible for several months, significantly impacting the security situation for developers and users. The Mini Shai-Hulud campaign, which began in May 2026, aimed to exploit vulnerabilities in various software development environments. The attackers used specific malware to gain access to sensitive data and jeopardize the integrity of software projects.
The return of the compromised GitHub Actions has reignited security concerns within the developer community. After the accessibility of the repositories was restored, it was quickly discovered that the malware was active again. Security researchers warned of the potential risks posed by the Mini Shai-Hulud malware, as it is capable of manipulating code and stealing confidential information. Consequently, the affected GitHub Actions were promptly disabled to prevent further damage. GitHub's response to the incidents was swift; however, the question remains as to how such security vulnerabilities can be prevented in the future.
Experts are calling for increased monitoring and security measures for open-source projects to avoid similar incidents. The developer community is urged to review and improve their security practices as necessary. The affected repositories now display the message: "Access to this repository has been disabled." This indicates that GitHub is taking proactive measures to protect the integrity of the platform. The security situation remains tense, as the threat of malware in software development persists. The Mini Shai-Hulud campaign has affected not only GitHub but also other platforms and tools in software development.
Security researchers have found that the attackers employ a variety of techniques to infiltrate systems and spread their malware. The complexity of the attacks necessitates comprehensive collaboration between developers, security researchers, and platform providers. The incidents have also sparked a discussion about the responsibility of platforms like GitHub. The need to implement security policies and educate users about potential risks is considered crucial. The developer community is called to remain vigilant and regularly install security updates.
The vulnerability exploited by the Mini Shai-Hulud campaign has the potential to have far-reaching effects on software development. Developers must be aware of the risks and take appropriate measures to protect their projects. The incidents underscore the importance of security awareness in today's digital landscape. The affected GitHub Actions were compromised in May 2026, leading to a comprehensive investigation of security practices on the platform. Security researchers and developers continue to analyze the impact of the malware and develop appropriate countermeasures. Experts assess the security situation as critical, as the threat of malware in software development continues to exist. The developer community is urged to review and improve their security practices to prevent future attacks.
💬 Comments (0)
No comments yet. Be the first to comment!