


CISA Warns of Flax Typhoon and New Vulnerabilities
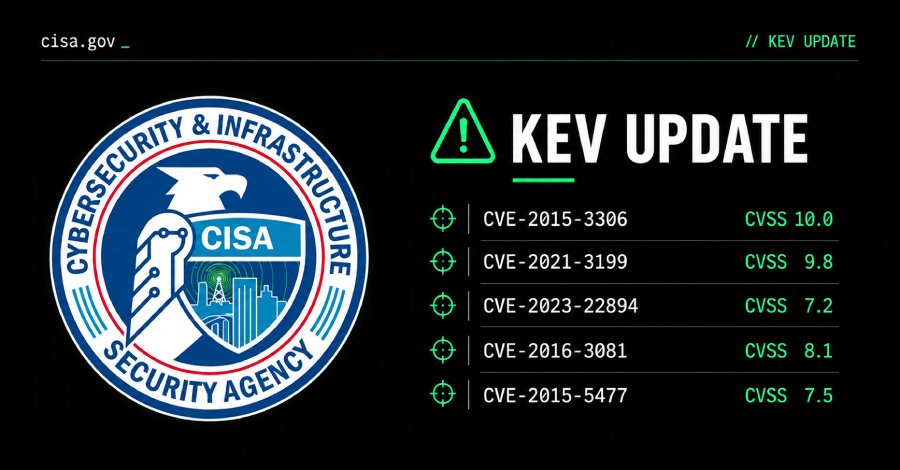
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog on October 11, 2026. This action is in response to the threat posed by the China-linked group Flax Typhoon, which is actively exploiting these vulnerabilities. The first vulnerability, CVE-2015-3306, has a CVSS score of 10.0 and affects ProFTPD.
This vulnerability allows unauthorized access to systems, potentially leading to severe security incidents. CISA has emphasized the urgency of this vulnerability as it has already been used in various attack scenarios. Additionally, CVE-2021-22986 has been identified, a critical vulnerability in F5 BIG-IP, which also has a CVSS score of 9.8. This vulnerability enables attackers to take control of affected systems, potentially resulting in complete data loss. CISA recommends that this vulnerability be patched immediately.
Another vulnerability, CVE-2022-26134, affects Atlassian Confluence and has a CVSS score of 9.8. This vulnerability can be exploited by attackers to execute arbitrary code on affected servers. CISA has urged affected organizations to take immediate action to protect their systems. The vulnerability CVE-2022-22965 in Spring Cloud also has a CVSS score of 9.8. This vulnerability allows attackers to bypass security mechanisms and gain unauthorized access to sensitive data.
CISA has stressed the severity of this vulnerability and recommends that the necessary updates be installed promptly. Finally, CVE-2022-22963 in Apache Tomcat has been identified, which has a CVSS score of 7.5. This vulnerability can lead to a denial-of-service attack, affecting the availability of services. CISA has called on organizations to check their systems for this vulnerability and implement appropriate security updates. CISA has set a deadline of October 11, 2026, by which all federal agencies must take the necessary steps to remediate these vulnerabilities. This deadline aims to ensure that critical infrastructures and government agencies are protected from potential attacks.
The threat group Flax Typhoon has previously conducted several high-profile attacks targeting vulnerabilities in widely used software. CISA warns that the group remains active and is developing new attack methods to circumvent security measures. CISA has urged affected organizations to review their security protocols and ensure that all systems are up to date.
The agency emphasizes that proactive measures to identify and remediate vulnerabilities are crucial for ensuring system security. The vulnerabilities exploited by Flax Typhoon are part of a larger trend where state-sponsored actors increasingly exploit vulnerabilities in critical infrastructures. Therefore, CISA has promoted collaboration between the private and public sectors to improve the response to such threats. CISA plans to regularly release updates on known exploited vulnerabilities to inform organizations about new threats and recommended security measures. The next update to the KEV catalog is scheduled for November 15, 2026.
💬 Comments (0)
No comments yet. Be the first to comment!