


Bitter Hackers Deploy PapRAT Backdoor in Cyber Attacks
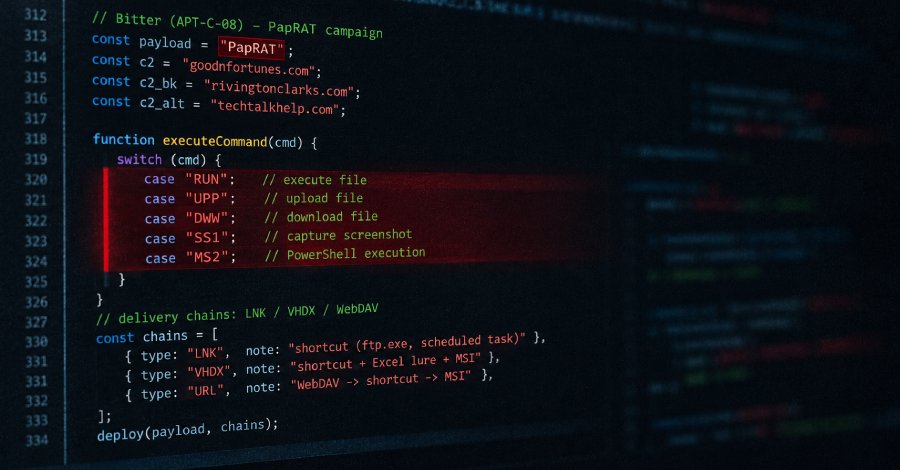
The South Asian cyber-espionage group Bitter, also known by the designations APT-C-08, APT-Q-37, Hazy Tiger, Orange Yali, T-APT-17, and TA397, has introduced a new threat in the form of a Remote Access Trojan (RAT) named PapRAT. This malware has been specifically designed to target organizations in South Asia and steal their data. Researchers from Fortinet FortiGuard Labs, including Cara Lin, have found that PapRAT is implemented in both C++ and Rust. This dual implementation allows attackers to deploy the malware in various environments and maximize its efficiency. The malware offers a variety of functions, including executing commands and accessing files.
Attacks by Bitter target a range of sectors, including government agencies, educational institutions, and businesses. These target groups are particularly vulnerable to cyber attacks as they often possess sensitive information that is of high interest to attackers. The use of PapRAT could enhance the group's ability to operate undetected and achieve their objectives. The malware employs various techniques to infiltrate the victims' systems, including phishing emails containing malicious attachments or links, as well as exploits of known security vulnerabilities in software.
These methods are not new; however, the introduction of PapRAT indicates that Bitter has evolved its tactics to counter the ever-changing security landscapes. Another notable feature of PapRAT is the ability to remotely control infected systems. Attackers can execute commands, download or upload files, and even take screenshots of the user interface. These capabilities enable attackers to gain comprehensive control over the affected systems and extract valuable information. The security community has already responded to the threat posed by PapRAT.
Security researchers and IT experts recommend that organizations regularly update their systems and review security policies to prepare against such attacks. Implementing layered security measures can help minimize the risk of a successful attack. The discovery of PapRAT is further evidence of the ongoing threat posed by state-sponsored hacker groups in the region. Bitter's activities are part of a larger trend where cyber attacks are increasingly used as a means of political and economic influence. The international community is observing these developments with concern, as they could jeopardize stability in the region.
The exact number of affected organizations and the impact of the attacks are currently unclear. However, security researchers are working to analyze the spread of PapRAT and develop countermeasures. The threat posed by this malware could intensify in the coming months as the group adapts its tactics and targets new victims. The vulnerability that PapRAT exploits may be discovered by other attackers in the coming weeks, underscoring the need for proactive security measures. Fortinet researchers warn that organizations in South Asia should remain particularly vigilant to protect themselves from this new threat. The PapRAT malware was first identified in November 2026 and poses a serious threat to cybersecurity in South Asia.
💬 Comments (0)
No comments yet. Be the first to comment!