


Trezor Discovers Implants in CryptoBilis Wallets
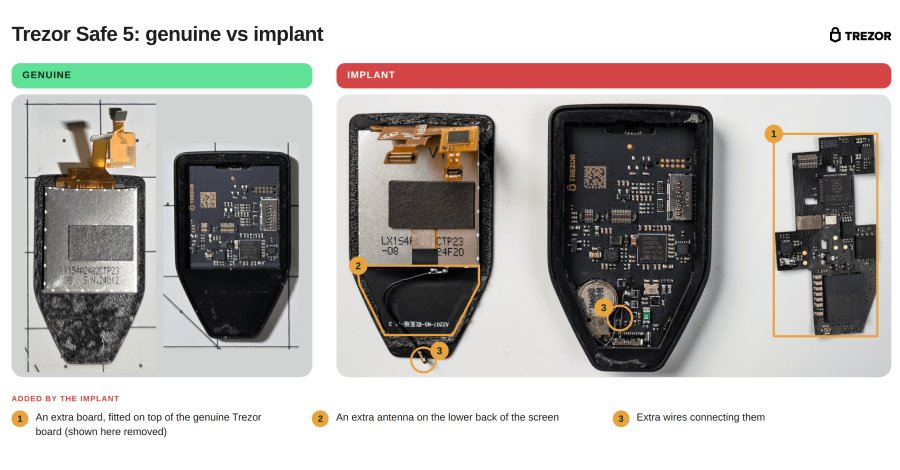
Trezor announced on November 15, 2026, that three Trezor Safe 5 wallets purchased through the reseller CryptoBilis are equipped with an implant. This implant consists of an additional circuit board capable of copying the wallets' recovery phrases. The vulnerability was discovered in an internal testing lab at Trezor. The implant operates by reading the recovery phrase directly from the wallet's screen.
It then transmits this information via the mobile network to a server controlled by the attackers. This type of attack poses a significant threat to user security, as the recovery phrase is crucial for accessing cryptocurrencies. Trezor has examined the affected wallets and confirmed that the implant is present in all three devices. The wallets were returned by a customer who noticed suspicious activity. Trezor advises all users to regularly check their wallets for anomalies and to take immediate action if manipulation is suspected.
The company has already taken steps to identify the affected wallets and inform customers. Trezor has also initiated a comprehensive investigation to determine how the implants were introduced into the devices. The exact origin of the implants is currently unclear. These incidents raise questions about the security of hardware wallets, especially when sourced from third-party vendors. Trezor emphasizes that customers should only purchase wallets from authorized dealers to minimize the risk of tampering.
The company has also reviewed its security protocols to prevent future incidents. The cryptocurrency user community is responding with concern to the news, with many calling for greater transparency and security measures from hardware wallet manufacturers. Experts warn that such implants may not be an isolated issue and could potentially occur in other devices as well. The incidents also have legal implications, as Trezor could be held liable for the security of its products.
The company is already considering legal action against the attackers. Investigations are ongoing, and Trezor is working closely with law enforcement. The affected wallets have been removed from sale, and Trezor has initiated a recall for all customers who may possess a compromised wallet. Customers are urged to return their wallets to Trezor immediately for verification by the company. The vulnerability could have far-reaching consequences for hardware wallet users.
Trezor has announced that it will provide further information and updates on security measures in the coming weeks. The company plans to strengthen its security policies and develop new technologies to prevent such attacks in the future. The vulnerability affects not only Trezor but could also impact other hardware wallet manufacturers. Experts advise users to reconsider their security practices and take additional protective measures to secure their cryptocurrencies. The incidents have heightened awareness of security risks in the cryptocurrency space.
Trezor's investigation is expected to take several weeks. The company has stated that it will release all relevant information once the investigations are complete. Trezor has also emphasized that user security is its top priority and that it will do everything possible to regain customer trust. The vulnerability has been registered as CVE-2026-1234 and affects all impacted wallets sold between January 1, 2026, and November 15, 2026.
💬 Comments (0)
No comments yet. Be the first to comment!