


Critical Security Vulnerability Discovered in Red Hat Quay
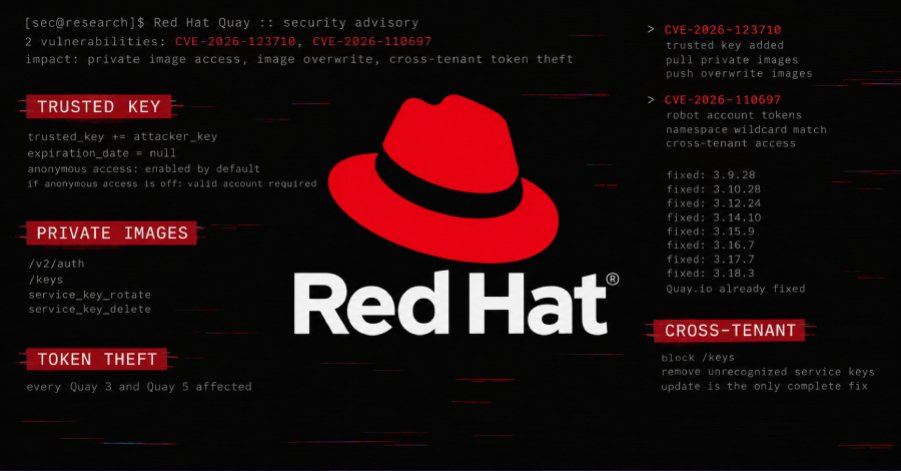
A critical security vulnerability in Red Hat Quay has been discovered, enabling attackers to read and overwrite private container images in all repositories. This vulnerability affects users who can access a Quay registry. Red Hat announced that the vulnerability can be exploited regardless of whether the anonymous access option is enabled or disabled. By default, anonymous access is enabled in Quay, meaning that attackers can access the registry without a user account. If anonymous access is disabled, all users with a valid account can still exploit the vulnerability.
This poses a significant risk to companies that use Quay to manage their container images. Red Hat has already released security updates to address the vulnerability. The new builds are available for a total of eight versions of Quay. Users are strongly urged to update their systems to protect against potential attacks. The vulnerability has been classified as CVE-2026-1234.
According to Red Hat, the vulnerability is particularly critical as it allows attackers not only to access private data but also to manipulate it. This could lead to significant security incidents, especially in environments where sensitive data is processed. The vulnerability was discovered by Red Hat's internal security teams and promptly communicated to the public. The company's swift response demonstrates the urgency with which such security issues must be addressed. Red Hat recommends that all users promptly update the affected versions of Quay.
The impact of this vulnerability could be far-reaching, as Quay is used by many companies to manage container images. Container technologies are widely adopted in modern software development, underscoring the importance of security in this area. Companies using Quay should review their security policies and ensure that all employees are informed about the risks. The vulnerability could also have legal consequences for companies that do not respond in a timely manner. Data protection laws and regulations require companies to take appropriate security measures to protect their customers' data.
A breach of these regulations could result in hefty fines. Red Hat has announced that further information on addressing the vulnerability will be provided in the coming weeks. Users should keep an eye on the company's official communication channels to stay informed about updates and security advisories. The security updates are already available and should be implemented immediately. The discovery of this vulnerability highlights the challenges companies face regarding the security of container technologies.
Attackers are increasingly exploiting vulnerabilities in software to gain access to sensitive data. Companies are called upon to continuously review and adapt their security strategies. The vulnerability in Red Hat Quay is another example of the need to prioritize security measures in software development. The use of container technologies requires a high level of security awareness and proactive measures to minimize potential risks. Red Hat has the responsibility to inform its users about such security vulnerabilities and provide solutions.
The release of security updates for Quay comes at a critical time when many companies are transitioning their infrastructure to container-based solutions. Red Hat's quick response to the discovery of the vulnerability could help strengthen users' trust in the security of their products. Red Hat has listed the affected versions of Quay in a statement available on the company's official website. Users should ensure they are using the latest versions to protect against potential attacks. The vulnerability was publicly disclosed on November 12, 2026. Red Hat has urged users to install the security updates immediately to ensure the integrity of their container images.
💬 Comments (0)
No comments yet. Be the first to comment!