


Cyber Attacks on Check Point Gateways: TSGA Backdoor Discovered
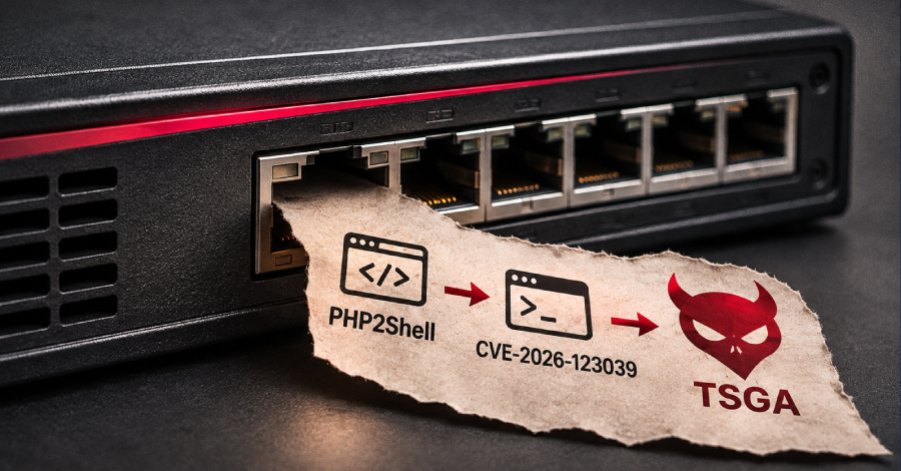
An unknown threat actor has been targeting unprotected Check Point Security Gateways since October 30, 2026. The attacks are aimed at Israeli organizations and exploit vulnerabilities in the PHP2Shell software to gain initial access. Following the initial compromise, an unreported local privilege escalation vulnerability in Gaia OS is exploited to install a backdoor named TSGA. The security firm Check Point has documented the attackers' activities and warns of the potential consequences of these attacks.
The PHP2Shell vulnerabilities allow attackers to take control of the affected systems, leading to a significant security risk. The exact number of affected systems is currently unknown; however, a broader target audience is assumed. The TSGA backdoor enables attackers to access sensitive data and potentially install further malware. The attackers appear to have specifically targeted organizations in Israel, indicating a possible political motivation. Check Point has informed the affected companies and strongly recommends checking all systems for the latest security updates.
Vulnerabilities in PHP2Shell are not new; however, the combination with local privilege escalation in Gaia OS has not been exploited until now. This discovery raises questions about the security of Check Point products, which are used in many companies worldwide. The security firm has already taken measures to protect the affected systems and address the vulnerabilities. The attacks are part of a growing number of cyber incidents targeting critical infrastructures. Experts warn that such attacks could increase in the future, especially if companies do not proactively enhance their security measures.
The threat of cyber attacks has significantly increased in recent years, highlighting the need to regularly review and update security protocols. The vulnerability in Gaia OS has not been specified in detail; however, it is known to allow attackers to escalate their privileges on compromised systems. This could lead to complete system access, jeopardizing data integrity and confidentiality. Check Point has already announced an update to address this vulnerability. The incidents have also attracted the attention of government agencies monitoring the security situation in the region.
The Israeli Cyber Security Authority has issued a warning, urging companies to harden their systems and report suspicious activities. The authority emphasizes the importance of training employees to recognize phishing attacks and other social engineering techniques. The discovery of these attacks and the associated vulnerabilities underscores the challenges companies face in the field of cybersecurity. The need to continuously evaluate and adapt security solutions is becoming increasingly urgent. Check Point has announced that it will provide further information about the attacks and the measures taken. The vulnerability in PHP2Shell carries the CVE number CVE-2026-XXXX, and the exact number of affected systems is currently being determined.
💬 Comments (0)
No comments yet. Be the first to comment!