


Critical Security Vulnerability in Python Library Pillow
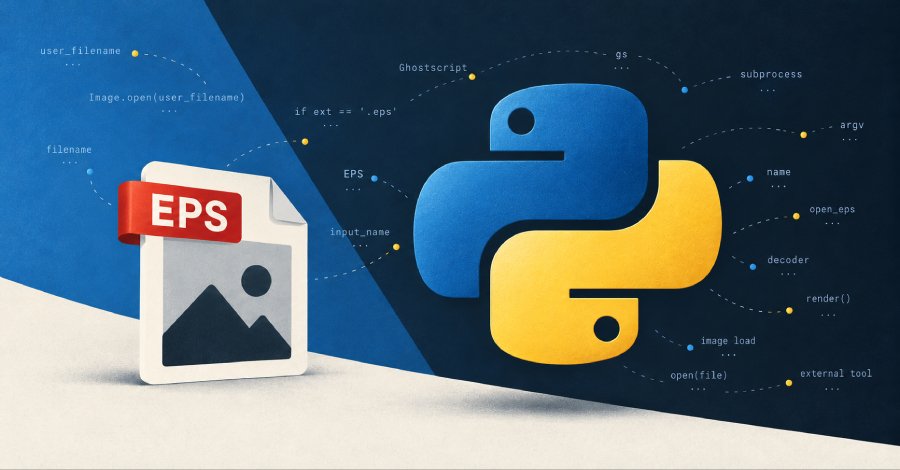
Pillow, the most widely used image library for Python, has discovered a critical security vulnerability that allows attackers to execute operating system commands on a server. This vulnerability, identified as CVE-2026-112900, affects the way Pillow processes EPS images. When opening these files, the filename is passed to Ghostscript without prior validation, leading to potential exploitation. The vulnerability has been found in the current version of Pillow, which is utilized by a variety of developers and companies worldwide. The ability to execute arbitrary commands poses a significant risk, especially for web applications that rely on this library.
Attackers could gain access to the underlying operating system by uploading a specially crafted EPS image. The vulnerability has been classified as critical by security experts, as it enables attackers to take control of servers using the affected library. This type of attack could lead to data loss, unauthorized access to sensitive information, and other serious consequences. Developers are urged to review their systems and take appropriate measures. The developer community has already responded to the discovery.
Many users of Pillow have begun to review their implementations and search for potential security gaps. The response to this vulnerability highlights the importance of security updates and regular dependency checks in software projects. To minimize the impact of this security vulnerability, experts recommend temporarily suspending the use of EPS images in applications that utilize Pillow. Additionally, developers should ensure they are using the latest version of the library that includes security updates. The developers of Pillow have announced that they are working on a patch to address the vulnerability.
The vulnerability affects not only developers but also companies that rely on image processing in their applications. The possibility that attackers could infiltrate systems through this vulnerability could have significant legal and financial consequences. Therefore, companies should take proactive measures to protect their systems. The discovery of this vulnerability underscores the need to strengthen security practices in software development. Developers should be aware that even widely used libraries like Pillow can be susceptible to security issues.
Implementing security checks and testing during the development process can help identify such vulnerabilities early. The security vulnerability CVE-2026-112900 was published on October 24, 2026, and has already caused a stir in the developer community. The exact number of affected systems is currently unknown; however, it is estimated that millions of applications worldwide rely on Pillow.
💬 Comments (0)
No comments yet. Be the first to comment!