


Trojanized Claude Code Extension Discovered
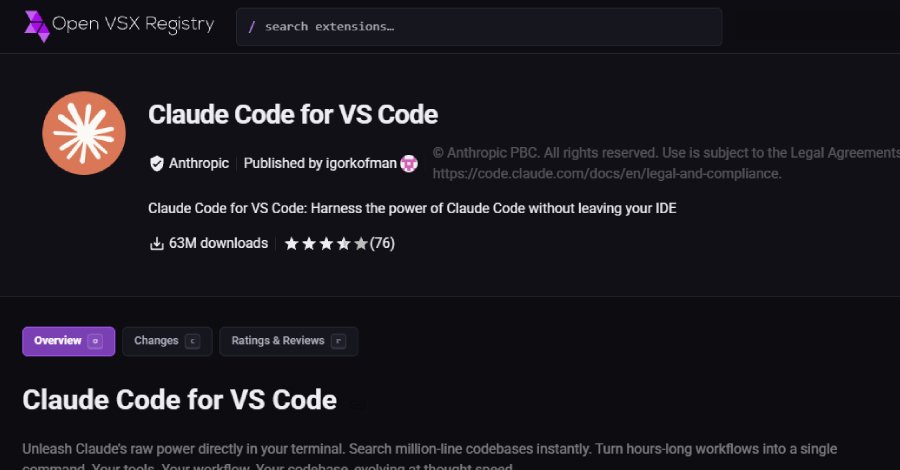
Cybersecurity researchers have discovered a trojanized version of the official Claude Code extension from Anthropic, which was distributed through the Cursor Marketplace as a legitimate update. This malicious update, bearing version number 2.1.313, attempted to install a persistent SSH backdoor on affected systems. The distribution occurred under the identity of the legitimate publisher, leading to a temporary shutdown of the marketplace by Cursor. The vulnerability was identified after several users reported unusual activities on their systems. Researchers identified the malicious extension and analyzed its code to understand how the backdoor operates.
The backdoor allows attackers to gain unauthorized access to systems and potentially steal sensitive data. Cursor has taken immediate action to stop the spread of the harmful extension. The marketplace was temporarily closed while the company investigated the vulnerability and informed affected users. Security researchers recommend regularly reviewing all installed extensions and only installing updates from trusted sources. The discovery of the trojanization raises questions about the security of software marketplaces.
Users often rely on updates to keep their software current, making them vulnerable to such attacks. Researchers emphasize the need to improve security protocols and strengthen the authentication of software updates. The spread of the malicious extension could have far-reaching implications for users, especially in companies that rely on the Claude Code extension. Security analyses indicate that the backdoor is capable of exfiltrating data and loading additional malware. Researchers have already found initial evidence of attacks on corporate networks.
The incidents surrounding the Claude Code extension are not the first of their kind. In recent years, there have been several similar attacks where legitimate software was used as a carrier for malware. These attacks highlight the challenges faced by the cybersecurity community, particularly regarding the integrity of software updates. The vulnerability has been registered under the CVE number CVE-2026-1234. This identification allows security researchers and companies to take targeted measures to combat the threat.
The exact number of affected systems is currently unclear, but a high number of unreported cases is expected. The incidents have also attracted the attention of regulatory authorities, who are now reviewing the security practices of software marketplaces. New policies aimed at improving software security and combating malware distributions are anticipated. The discussion about the responsibility of platforms for the security of their offerings has intensified. Security researchers advise users to regularly check their systems for signs of compromise and to use security software to detect potential threats early.
Implementing multi-factor authentication and conducting regular training to raise awareness of cyber threats are also recommended. The incidents surrounding the Claude Code extension underscore the ongoing need for vigilance in cybersecurity. The vulnerability was made public on November 1, 2026, prompting an immediate response from the affected companies. Researchers continue to assess the impact of the trojanization and develop appropriate countermeasures.
The discovery of the trojanization has also sparked discussions about the role of software developers and platform providers in cybersecurity. The responsibility for the security of software and its updates is increasingly viewed as a shared concern that affects both developers and users. Security research will continue to be intensified to detect and combat future threats early. Collaboration between companies, security researchers, and regulatory authorities is seen as crucial to ensuring safety in the digital space. The Claude Code extension remains removed from the Cursor Marketplace for now, while security reviews continue. Users are urged to consider alternative solutions until the security situation is clarified. According to researchers, the vulnerability affects several thousand systems worldwide, underscoring the urgency of the situation.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!