


Security Risk from Browser Extensions for Claude
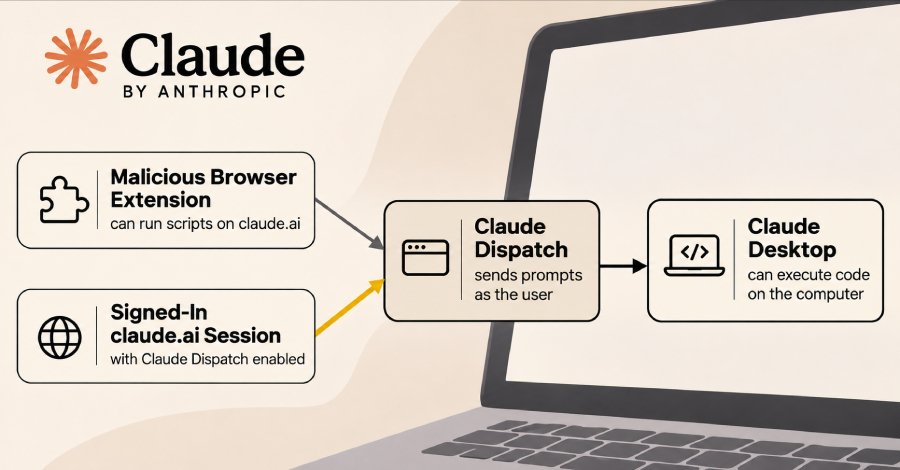
Research by Forever Security has revealed that a vulnerability in the browser extension for Claude allows attackers to execute malicious scripts on users' computers. This weakness exploits the Dispatch function of Claude, which enables users to send tasks from their smartphones to Claude Desktop. The researchers demonstrated that an attacker could gain access to the functions of Claude Desktop through a manipulated browser extension. This is achieved by injecting malicious code into the communication between the smartphone and the desktop. The security flaw could allow attackers to access sensitive data or install harmful software.
The vulnerability has been mentioned in previous reports, but it remains exploitable to this day. Forever Security has pointed out that attackers do not require special permissions to carry out this attack. This increases the risk for a wide range of users who utilize the Claude platform. The researchers recommend that users regularly review their browser extensions and only install those from trusted sources. The use of security software is also advised to detect and fend off potential threats early.
The security vulnerability could have serious consequences, especially for companies that use Claude for business purposes. The exact number of affected users is currently unknown; however, the widespread use of Claude Desktop in combination with the vulnerability could endanger a large number of systems. Forever Security has classified the vulnerability as critical and recommends immediate measures for risk mitigation. Claude, a product of Anthropic, has gained popularity in recent years, particularly in the field of artificial intelligence. The Dispatch function is frequently used to facilitate interaction between mobile devices and desktop applications.
The security vulnerability could significantly undermine trust in the platform. Researchers from Forever Security have already contacted the developers of Claude to bring attention to the security issue. However, there has been no official statement or solution from Anthropic so far. Users are urged to remain vigilant and regularly check their systems for suspicious activities.
The vulnerability could also impact the future development of Claude, as the company may need to implement additional security measures to regain user trust. The researchers have emphasized that the implementation of security protocols in software development is crucial to avoid such vulnerabilities. The flaw identified by Forever Security could be classified as CVE-2026-XXXX once it is officially recognized. The exact designation and details of the vulnerability are expected to be released in the coming weeks.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!