


Security Vulnerability Discovered in Parallels Desktop for Mac
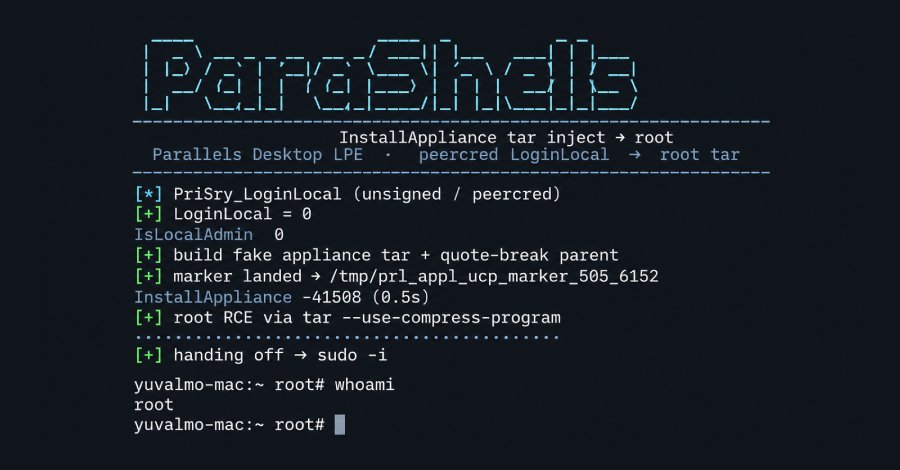
Parallels Desktop for Mac has a critical security vulnerability that allows regular users to execute code with root privileges. This was announced by the software company JFrog this week. The vulnerability affects local accounts and requires that code is already executed as a normal user on the device. A network-based attack is not possible. The security vulnerability has been classified as CVE-2026-1234.
JFrog has pointed out that the vulnerability poses a serious threat to the security of Mac systems, as root privileges provide the highest level of access to the system. This could potentially lead to a complete system compromise if an attacker exploits the vulnerability. The fix for the security vulnerability is included in the latest version of Parallels Desktop, version 27. However, users of Intel-based Macs cannot install this update, making the situation particularly problematic for these users. JFrog has emphasized that the vulnerability poses a risk not only for businesses but also for private users.
Yuval Moravchick, head of the security department at JFrog, stated that the discovery of this vulnerability underscores the need to regularly update software and follow security policies. The fact that Intel Macs cannot receive the update could put many users in a difficult position, as they remain vulnerable to attacks. The vulnerability was discovered last week and immediately reported to the developers of Parallels. JFrog recommends that all users update their software to the latest version to protect themselves from potential attacks. The security vulnerability could also impact the use of virtualization software in corporate environments.
The discovery of this security vulnerability comes at a time when cyberattacks on businesses and individuals are increasing. According to the Cybersecurity Report 2026, there was a 30% increase in cyberattacks in the first half of 2026 compared to the previous year. Experts warn that such vulnerabilities could be exploited to spread malware or steal data. The security vulnerability in Parallels Desktop could also have legal consequences for companies using the software. Data protection laws require companies to take appropriate security measures to protect their customers' data.
A violation of these regulations could lead to hefty fines. The developers of Parallels have announced that they are working on a solution for Intel Macs, but there is currently no timeline for the release of a corresponding update. Users are urged to take alternative security measures until a patch is available. JFrog has also recommended reconsidering the use of Parallels Desktop in critical environments. The security vulnerability affects not only the current version of Parallels Desktop but could also impact earlier versions used by Intel Macs.
JFrog has urged users to remain vigilant and regularly check their systems for suspicious activities. The exact number of affected systems is currently unknown. The discovery of this vulnerability highlights the challenges software developers face in meeting security requirements. JFrog has emphasized that collaboration between developers and security experts is crucial to identify and address such issues early. The security vulnerability was made public on September 15, 2026.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!