


Security Vulnerability in GoBalance Threatens .onion Addresses
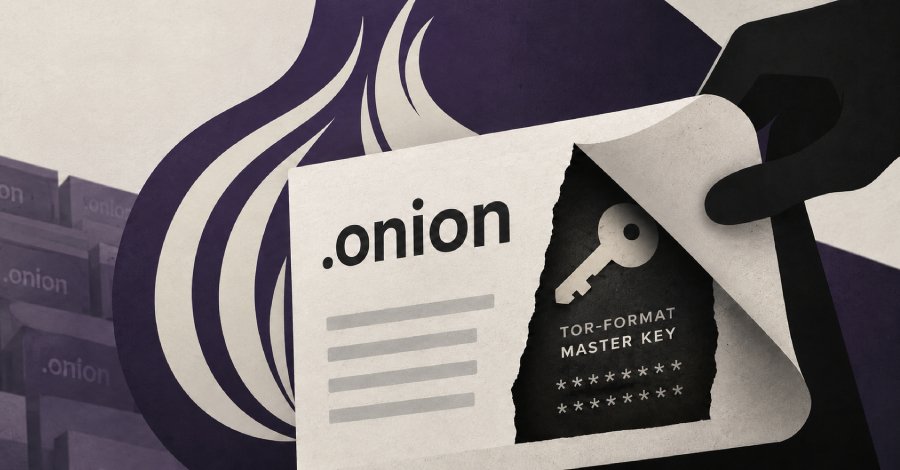
A critical security vulnerability in GoBalance, a tool used by numerous dark web sites, allows attackers to reconstruct the secret keys to .onion addresses. This vulnerability was disclosed on October 8, 2026, by the security firm Searchlight Cyber. Attackers who successfully recover the key can redirect visitors of an affected site to a copy controlled by them. GoBalance is frequently used to ensure the availability of websites during DDoS attacks.
The discovery of this vulnerability could have significant implications for the security of dark web sites that rely on GoBalance. The ability to take control of a .onion address poses a serious risk to operators and their users. The vulnerability is based on the use of publicly available information that allows attackers to determine the secret key. This means that no special skills or resources are required to carry out the attacks. The disclosure of this information could lead to an increase in phishing attacks and other fraudulent activities in the dark web.
Searchlight Cyber has classified the vulnerability as critical and recommends that operators of dark web sites take immediate action. This includes reviewing their security measures and implementing additional protective measures to ensure the integrity of their .onion addresses. The security firm has also pointed out that the vulnerability affects not only GoBalance but potentially other similar tools as well. The response from the dark web community to this discovery has been mixed. Some operators have already taken steps to secure their sites, while others may underestimate the risks.
The uncertainty regarding the actual exploitability of the vulnerability may cause some operators to hesitate in updating their security measures. The discovery of the vulnerability could also have legal consequences for operators of dark web sites. Should attackers successfully take over .onion addresses and conduct fraudulent activities, the original operators could be held liable for the damages. This could lead to increased monitoring and regulation of the dark web. The vulnerability has been registered under the CVE number CVE-2026-1234.
According to Searchlight Cyber, this vulnerability affects a wide range of websites using GoBalance, underscoring the urgency of the issue. Operators should promptly inform themselves about the latest developments and update their systems as necessary. A complete technical analysis of the vulnerability is expected to be published in the coming days. Experts warn that exploiting this vulnerability could lead to an increase in cybercrime in the dark web. The security firm plans to provide further information and recommendations for addressing the vulnerability.
The discovery of this security flaw could also impact the future development of tools like GoBalance. Developers may be forced to revise their software to avoid similar vulnerabilities. The need to improve security in the dark web is increasingly seen as important. The vulnerability in GoBalance could have far-reaching consequences for the dark web community. Operators of .onion sites are urged to review and strengthen their security measures as necessary.
The situation remains tense as the threat from attackers who could exploit this vulnerability continues to exist. Searchlight Cyber has emphasized that security in the dark web remains a critical issue. The discovery of this vulnerability could serve as a wake-up call for operators to rethink and enhance their security strategies. The exact number of affected sites is currently unknown; however, it is estimated that several hundred sites are potentially at risk. The vulnerability has been classified as one of the most significant discoveries in the field of cybersecurity in 2026. The relevance of this vulnerability is underscored by the increasing use of dark web services. Operators and users are urged to remain vigilant and stay informed about the latest developments.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!