


Security Vulnerability Discovered in ChatGPT's Lockdown Mode
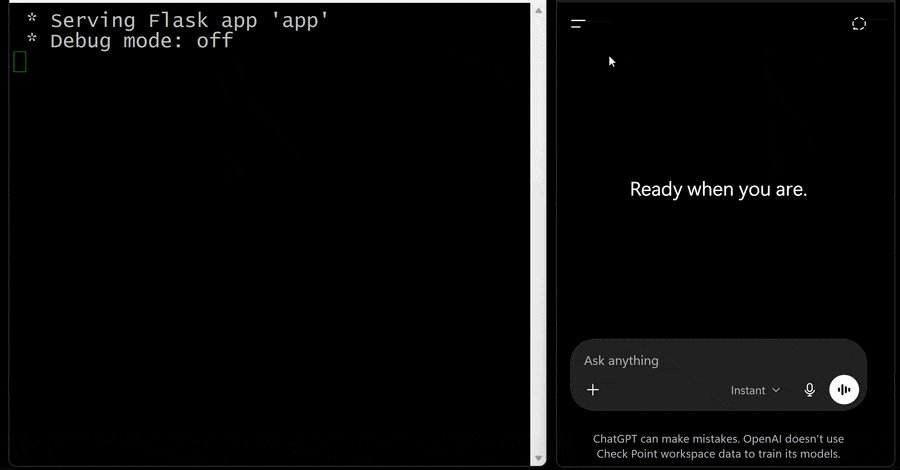
Cybersecurity researchers have published details of a security vulnerability that allowed the Lockdown Mode of OpenAI ChatGPT to be bypassed. This feature was introduced in June 2026 to minimize the risk of data exfiltration through prompts. The vulnerability could enable attackers to steal data from chats without the user's knowledge. The security flaw was classified as critical, as it could potentially be exploited for phishing attacks and other forms of data misuse. Researchers reported that the vulnerability allowed attackers to access sensitive information stored in the chats.
OpenAI has since addressed the vulnerability and provided an update to ensure the security of the system. The discovery of the security flaw raises questions about the effectiveness of security measures in AI applications. The Lockdown Mode was originally intended to protect user privacy and maintain data integrity. The fact that these protective measures could be circumvented demonstrates that continuous reviews and updates are necessary to minimize security risks. OpenAI emphasized in a statement that user security is of utmost priority.
The company is working closely with security experts to identify and address potential vulnerabilities early on. The researchers who discovered the flaw have been recognized for their work and granted access to additional security resources from OpenAI. The vulnerability has been classified under CVE-2026-XXXX, with the exact number yet to be released. This classification allows other security researchers to identify the flaw and understand how it was resolved. The discovery could also impact other AI applications that have implemented similar security mechanisms.
The discussion surrounding the security of AI systems is reignited by this discovery. Experts warn that the increasing complexity of AI applications could create new attack vectors. The necessity to regularly review and adjust security protocols is seen as crucial to maintaining user trust in such technologies. OpenAI plans to release further security updates in the coming months to ensure the integrity of its systems. The company has already announced that it will invest additional resources into the research and development of security solutions.
These measures are intended to help minimize the risk of data exfiltration and other security incidents. The vulnerability was discovered by a team of researchers specializing in the analysis of AI security protocols. Their findings were published in a journal focused on cybersecurity. The publication aims to assist other researchers in identifying and addressing similar vulnerabilities in other systems. The exact number of affected users is currently unknown; however, it is estimated that millions of users worldwide could be impacted by the security flaw.
OpenAI has already taken steps to inform affected users and assist them in protecting their data. The company has also set up a hotline to address user questions and concerns. The security vulnerability was officially reported on November 1, 2026, and the update to fix it was provided within 48 hours. OpenAI has stressed that a swift response to security incidents is crucial to maintaining user trust and ensuring the security of its systems.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!