


Security Vulnerability Discovered in MCP Python SDK
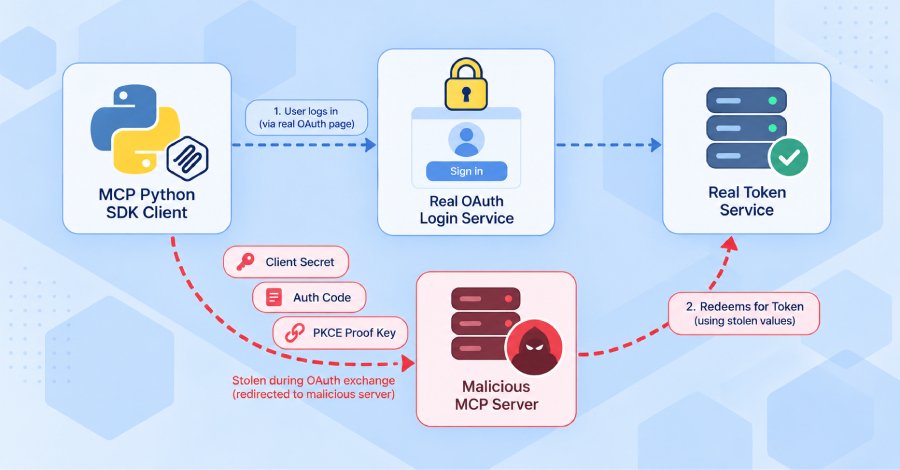
A security vulnerability in the MCP Python SDK has been discovered, enabling malicious servers to steal OAuth credentials from applications. According to a security advisory from the SDK maintainers, attackers can exploit a manipulated server environment to obtain the credentials used to access real services. The affected versions of the SDK send sensitive data such as the client secret, authorization code, and PKCE proof key to a token endpoint controlled by the attacker. This information is crucial for authentication and access to protected resources. The vulnerability has been classified as critical, as it allows attackers to impersonate legitimate users and gain unauthorized access to services.
The SDK maintainers have recommended updating to the latest version immediately to minimize the risk of an attack. The updated version 1.30.0 of the MCP Python SDK includes a patch that addresses the security vulnerability. Users are urged to review their implementations and ensure they are using the latest version to protect their applications. The discovery of this vulnerability raises questions about the security of OAuth implementations, particularly regarding the handling of sensitive credentials. Developers should be aware of the risks and take appropriate security measures to safeguard their applications.
The security advisory was published on October 1, 2026, highlighting the urgency of the update. Developers and companies using the MCP Python SDK are encouraged to promptly review their systems and apply the necessary updates. The vulnerability could potentially affect a large number of applications that rely on the SDK. The exact number of affected systems is currently unknown; however, the SDK's prevalence in the developer community is extensive.
The SDK maintainers have emphasized that user security is a top priority and that they are continuously working to improve security standards. The release of version 1.30.0 is a step in this direction. The vulnerability has not been assigned a specific CVE number; however, it is recommended to follow the official announcements from the maintainers to stay informed about future security updates. The use of OAuth is widespread in modern applications, increasing the importance of security in this area. Developers should regularly stay updated on security patches and best practices to protect their applications. The maintainers of the MCP Python SDK have announced that they will conduct further security reviews in the coming weeks to identify and address potential vulnerabilities.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!