


Security Vulnerability in Claude Code: 1,122 GitHub Repositories Affected
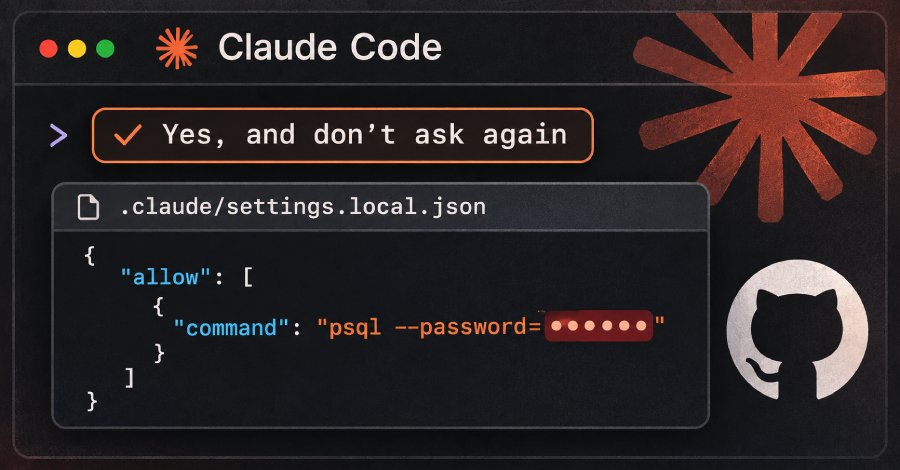
Passwords and API keys entered by developers in commands are accessible in 1,122 public GitHub repositories. This security vulnerability was caused by the "Yes, and don't ask again" feature in Anthropic's AI coding assistant, Claude Code. When users select this option, the system saves the command along with sensitive information in a project file. The security firm Apiiro highlighted this issue on November 7, 2026.
According to Apiiro, attackers can easily obtain sensitive data by accessing these public repositories, posing significant security risks for the affected projects. The discovery of this vulnerability raises questions about data security and the handling of sensitive information in software development. Developers using Claude Code are urged to review their projects on GitHub and ensure that no sensitive data is publicly accessible. Apiiro recommends disabling the feature that allows command saving to prevent future security incidents. An analysis of the affected repositories shows that a variety of projects in different programming languages are impacted.
The vulnerability could also affect the use of Claude Code in enterprises, as many organizations rely on this technology to optimize their development processes. The possibility of confidential information ending up in public repositories could undermine trust in such AI-powered tools. Developers and companies must be aware of the risks and take appropriate measures. The issue is compounded by the fact that many developers may not be adequately informed about the risks associated with using AI coding assistants. Apiiro has emphasized that training and awareness regarding security issues in software development are essential.
The security firm plans to provide further information and recommendations to support the developer community. The discussion about the security of AI-powered tools is expected to intensify, especially concerning the increasing prevalence of such technologies in software development. Experts warn that without proper security precautions, the risk of data leaks and cyberattacks increases. The industry faces the challenge of finding a balance between innovation and security. The incidents surrounding Claude Code are not the first to indicate vulnerabilities in AI-powered tools.
Similar issues have been identified in the past with other platforms, underscoring the need to establish and monitor security standards. The developer community is urged to take proactive measures to ensure the integrity of their projects. Apiiro has announced that it will continue to monitor the situation and provide updates on the affected repositories. The security firm plans to conduct a comprehensive analysis of the incidents to determine the causes of the vulnerability and develop solutions.
The results of this analysis are expected to be published in the coming weeks. The security vulnerability in Claude Code could have far-reaching consequences for software development, especially if developers do not pay attention to the risks associated with using AI tools. The industry must prepare for the challenges that come with integrating AI into the development process. According to Apiiro, over 1,000 repositories are already affected, highlighting the urgency of the situation.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!