


Security Research: OpenAI Accounts Compromised
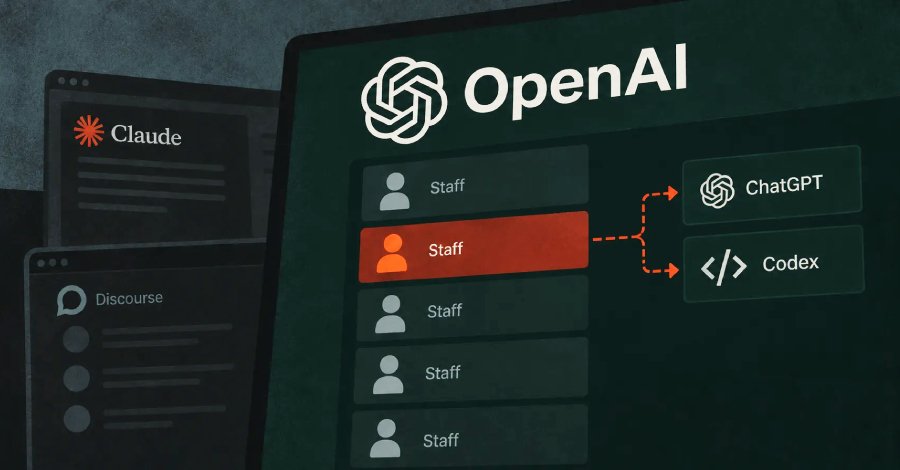
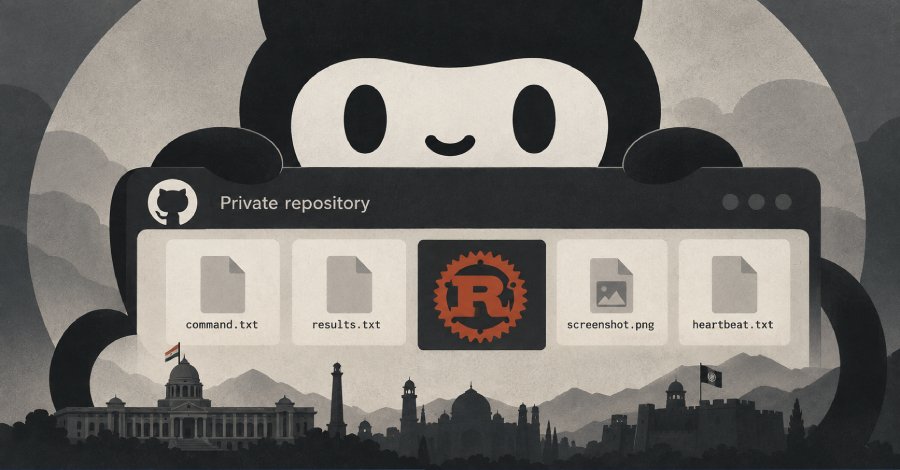
Three researchers from the security firm Hacktron exploited five security vulnerabilities at OpenAI with the help of Anthropic's Claude Opus 5. They were able to take over the accounts of several OpenAI employees, including those of ChatGPT and Codex. This security research led to access to an internal code repository of OpenAI. The attack began with a vulnerability in the software of OpenAI's public help forum, which allowed the researchers to breach the system.
Subsequently, they exploited another vulnerability in OpenAI's login system to take over the employees' accounts. The researchers documented the entire process to identify and analyze the security gaps. This type of research is crucial for recognizing vulnerabilities in software before they can be exploited by malicious actors. The discovery of these gaps could lead to improvements in security protocols at OpenAI. OpenAI has responded to the incidents and is working on addressing the identified vulnerabilities.
The company has emphasized that it takes the security of its systems seriously and is continuously working to enhance security measures. The Hacktron researchers have already submitted their findings to OpenAI. The vulnerabilities that were exploited are not the first to be discovered at OpenAI. In the past, there have been reports of similar incidents that pointed to weaknesses in the company's infrastructure. These incidents have reignited the discussion about the security of AI systems and their protection against attacks.
The use of Claude Opus 5 for this type of research demonstrates how advanced AI models can be employed in security research. Claude Opus 5 is known for its ability to analyze complex problems and find solutions. These capabilities were effectively utilized by the Hacktron researchers to identify the vulnerabilities at OpenAI. Security research has gained importance in recent years, especially in the field of AI. Companies are increasingly required to secure their systems against potential attacks.
Incidents at OpenAI could serve as a wake-up call for other companies in the industry to review and strengthen their security measures. The Hacktron researchers have emphasized that their work was not aimed at causing harm but rather at improving the security posture at OpenAI. They hope that their discoveries will contribute to raising security standards across the industry. The exact number of affected accounts has not been disclosed by OpenAI. The vulnerability in OpenAI's help forum has been classified as critical, meaning it could potentially have severe consequences for the security of user accounts.
OpenAI has announced that it will provide comprehensive security updates in the coming weeks to address the identified vulnerabilities. The Hacktron researchers have summarized their findings in a report that also includes recommendations for improving security practices. This report could serve as a guide for other companies facing similar security challenges. The publication of the report is scheduled for October 15, 2026.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!