


Ransomware Attacks: Experts Warn of CEO Mistakes
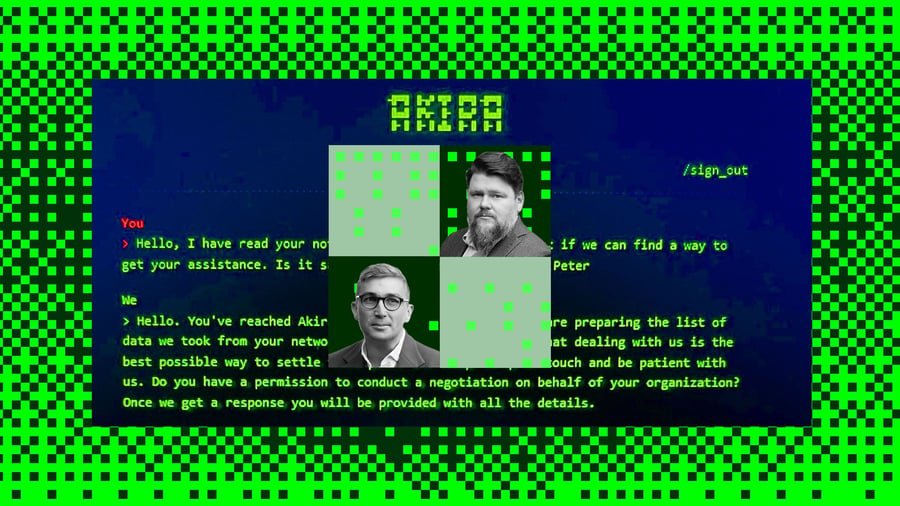
Cyber attacks, particularly from ransomware, have significantly increased in recent years and are increasingly affecting medium-sized enterprises. Experts warn that the worst mistake a CEO can make is to ask, "How do I pay?". This mindset can put companies in an even more precarious position, as it signals to the extortionists that they are willing to pay. The impacts of such attacks are severe. According to a recent study, 45% of surveyed companies have experienced at least one ransomware attack in the past two years.
The consequences range from production downtime to significant financial losses. Industries such as manufacturing are particularly affected, where downtime can directly lead to revenue losses. Experts recommend that companies take proactive measures to protect themselves against ransomware attacks. This includes implementing regular security updates and training employees to handle potential threats. A well-trained team can often recognize and fend off phishing attempts and other attacks early on.
Another important aspect is the creation of an emergency plan. Companies should have clear guidelines on how to respond in the event of an attack. This also includes not immediately focusing on paying a ransom but first analyzing the situation and restoring IT security. Negotiating with extortionists is a delicate matter. Experts advise against accepting the initial demand and instead maintaining a cool head.
Often, the initial ransom demands are inflated and can be lowered through skilled negotiations. An experienced cybersecurity consultant can provide valuable support in this regard. The legal framework for dealing with ransomware is also complex. In many countries, paying a ransom is not illegal; however, it can have legal consequences, especially if the extortionists are linked to criminal organizations. Therefore, companies should seek legal advice in a timely manner.
The cybersecurity landscape is constantly evolving. According to the Cybersecurity & Infrastructure Security Agency (CISA), there was a 30% increase in ransomware attacks in 2025 compared to the previous year. This increase requires companies to continuously review and adjust their security strategies. Another trend is the rise of Ransomware-as-a-Service (RaaS), where cybercriminals offer their attacks as a service. This lowers the entry barriers for potential attackers and leads to further proliferation of ransomware.
Companies must be aware of this threat and take appropriate measures. Investing in modern security solutions is crucial. Technologies such as artificial intelligence and machine learning can help detect and respond to threats in real-time. Companies that implement such technologies can significantly reduce their response times and minimize potential damage.
The necessity to prepare against ransomware is also recognized by the federal government. In 2026, the government plans to introduce a new law to strengthen cybersecurity in companies, which will include stricter requirements for IT security. "The best defense against ransomware is good preparation and a clear emergency plan," says a leading cybersecurity expert. "Companies must understand that they are not just victims but must also act proactively to protect themselves."
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!