


Malicious npm Packages Target WhatsApp Users
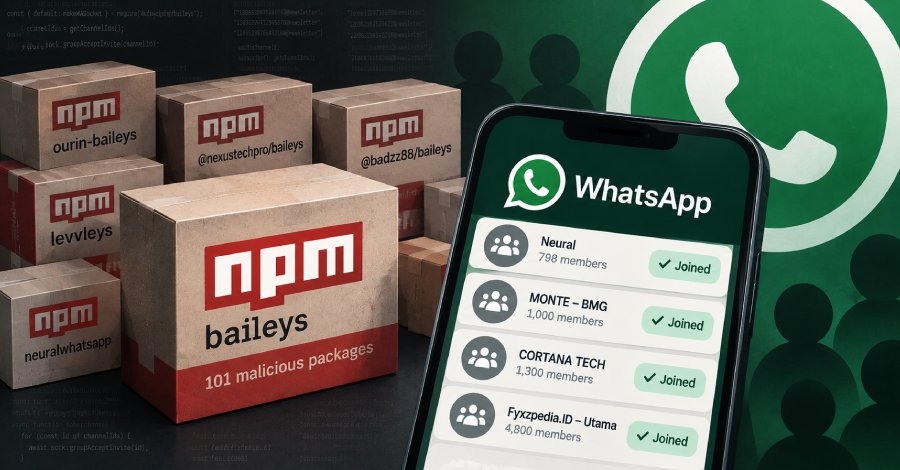
Cybersecurity researchers have identified a group of 101 malicious npm packages that involve developers in a WhatsApp group subscription campaign called PhantomSub. These packages exploit WhatsApp's Baileys open-source project to add victims to groups without their consent. The discovery was published by researchers Nir Zadok, Moshe Siman Tov Bustan, and Vitalii Chepurko from OX Security. The malicious packages are designed to abuse the WhatsApp API to integrate users into groups they did not create themselves. This is achieved by manipulating functions within the Baileys project, which was originally intended for developing WhatsApp bots.
The researchers warn that this technique not only jeopardizes user privacy but also the integrity of the platform itself. The affected npm packages have been used in various projects, amplifying the spread of the issue. Developers who have integrated these packages into their applications may unknowingly have become part of this campaign. The security researchers recommend regularly checking all npm packages for malicious activities and immediately removing any suspicious packages. The PhantomSub campaign is not the first of its kind to alarm the security community.
Similar incidents have been documented in the past, with malicious packages appearing in popular repositories. The researchers emphasize the need to improve security practices in software development to prevent such attacks. OX Security has published a detailed analysis of the affected packages to help developers better understand the risks. The analysis also includes technical details about the specific functions used by the malicious packages to manipulate users. Developers are urged to review the packages they use and ensure they come from trusted sources.
The security landscape in software development remains tense, as more attackers attempt to exploit vulnerabilities in popular tools. Researchers advise regularly installing security updates and following best practices in software development. A proactive approach can help minimize risks and ensure the security of applications. The discovery of these malicious packages has also drawn the attention of platform operators. npm, as one of the largest repositories for JavaScript packages, has taken measures to enhance the security of its platform.
These measures include regular security audits and the implementation of mechanisms to detect and remove malicious packages. The researchers from OX Security have also pointed out that the community plays a crucial role in combating such threats. Developers should actively participate in reporting suspicious activities and sharing information about malicious packages. An informed and engaged community can help improve security in the software ecosystem.
Security research will continue to play a critical role in identifying and combating threats. The researchers from OX Security have announced that they will continue their work and conduct further analyses to better understand the impacts of such attacks. The next publication is scheduled for October 15, 2026.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!