


Research Reveals RCE Exploits in Databases
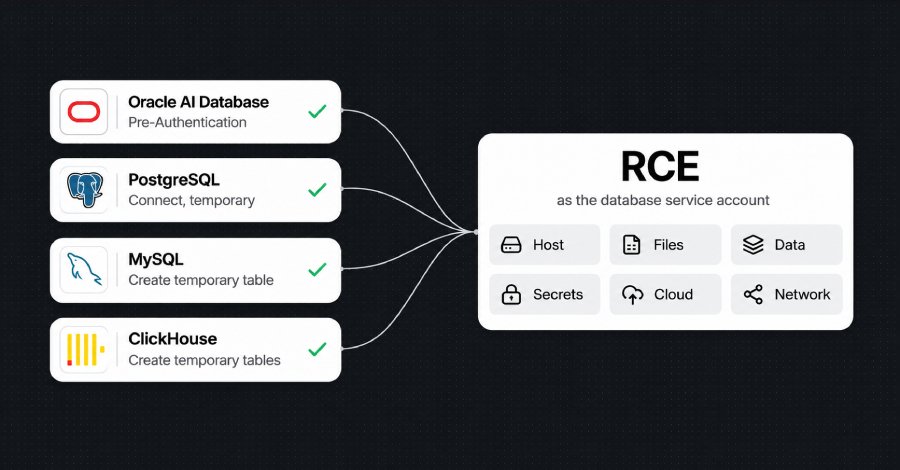
A researcher recently disclosed vulnerabilities in popular database management systems such as PostgreSQL, MySQL, and Oracle. These vulnerabilities allow for Remote Code Execution (RCE) to be performed, even when the database accounts used have minimal permissions. The findings were published on November 19, 2026, and show that even accounts without access to user tables can execute code on the database server. The released proof-of-concept exploits leverage specific memory corruption bugs in the SQL database engine code.
These bugs can be triggered through regular SQL queries, significantly increasing the attack surface. The researcher demonstrated the vulnerabilities in PostgreSQL, MySQL, and ClickHouse, while a separate exploit chain for Oracle was presented that does not require special permissions. The vulnerabilities have been classified as critical, as they enable attackers to take control of the database server. This could lead to data loss, unauthorized access to sensitive information, or even a complete compromise of the server. The discovery of these vulnerabilities raises serious questions about the security of database applications used by many companies worldwide.
The affected database vendors have already been informed about the vulnerabilities. PostgreSQL, MySQL, and Oracle have regularly released security updates in the past to address similar issues. Researchers recommend that administrators promptly update their systems to the latest versions to protect against potential attacks. The discovery of these exploits could also impact the development of security policies within organizations. Many organizations rely on databases to store and manage critical information.
The possibility that even low-privileged accounts can be exploited for attacks may lead companies to reconsider their access policies and implement stricter controls. The release of the exploits has already caused a stir in the security community. Experts warn that attackers could quickly exploit these vulnerabilities before patches are made available. The urgency of implementing security updates is regarded by many professionals as a top priority to minimize potential damage. The vulnerability affects not only large enterprises but also small and medium-sized businesses, which often allocate fewer resources to IT security.
Researchers emphasize that all organizations using these databases should be aware of the risks and take appropriate measures to protect their systems. The exact number of affected systems is currently unknown; however, it is estimated that millions of database instances worldwide could be potentially vulnerable. The vulnerability could also impact cloud database services that rely on these technologies. Researchers advise regularly reviewing security policies and providing training for employees to raise awareness of such threats. The vulnerabilities have been registered under the CVE IDs CVE-2026-XXXX for PostgreSQL, CVE-2026-YYYY for MySQL, and CVE-2026-ZZZZ for Oracle. The exact release of patches is expected from the respective vendors to address the vulnerabilities and ensure the security of the systems.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!