


Elementor Security Vulnerability Allows Website Takeover
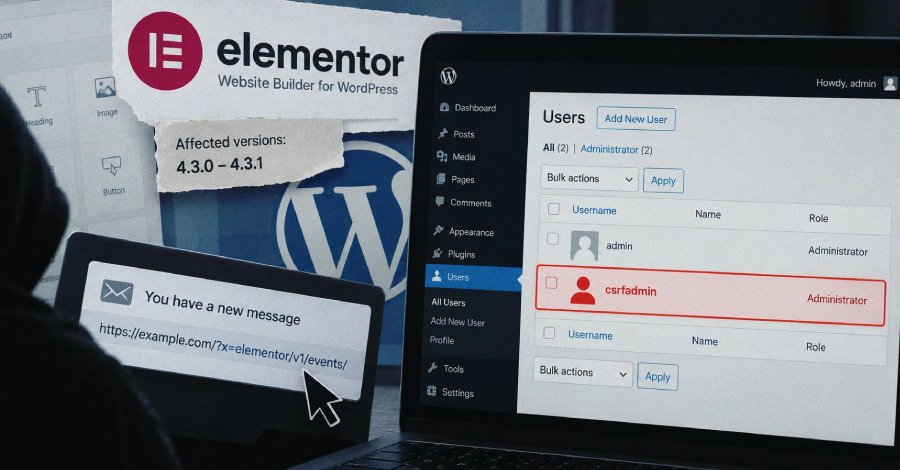
A serious security vulnerability in the Elementor Website Builder, a popular WordPress plugin, has been discovered. This Cross-Site Request Forgery (CSRF) weakness allows attackers to create malicious administrator accounts without authentication and take control of affected websites. The vulnerability has a CVSS score of 8.8 on a scale of 10 and affects specific versions of the plugin. Security experts have identified the vulnerability, noting that it can be exploited by clicking on a crafted link. This means that an unsuspecting administrator who clicks on the link could unwittingly hand over control of their website to an attacker.
The exact version of the plugin that is affected has not yet been disclosed. The developers of Elementor have not yet assigned an official CVE number for this vulnerability. However, security researchers strongly recommend that all affected versions of the plugin be updated immediately to minimize the risk of an attack. The exact number of affected websites is currently unknown, but it is estimated that Elementor is used on millions of websites worldwide. The discovery of this vulnerability comes at a time when cyberattacks on websites and online services are increasing.
According to the Cybersecurity & Infrastructure Security Agency (CISA), there was a 30% increase in reported security incidents in 2025 compared to the previous year. These figures highlight the urgency of quickly addressing vulnerabilities in widely used software. The Elementor developers have announced that they are working on a patch to fix the vulnerability. Until the update is released, it is recommended to reconsider the use of the plugin or implement additional security measures to protect websites. This includes using security plugins that can provide additional layers of protection.
The security community has already responded to the discovery and is urging website operators to regularly check their systems for vulnerabilities. Experts advise monitoring website logs to detect suspicious activities early. Quick action can help minimize potential damage. The Elementor security vulnerability is not the first of its kind. There have been several similar incidents in the past, underscoring the need for a proactive security strategy.
Website operators should be aware that the security of their platforms depends on regularly updating their software. The exact release date of the patch will be announced by Elementor. Security experts recommend following the company's official channels to stay informed about updates. If left unaddressed, the vulnerability could have significant implications for the security of websites relying on Elementor. The vulnerability could potentially jeopardize thousands of websites that use Elementor. According to estimates, over 5 million websites utilize the plugin, highlighting the urgency of the situation.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!