


Critical Security Vulnerability Discovered in Unbound DNS Resolver
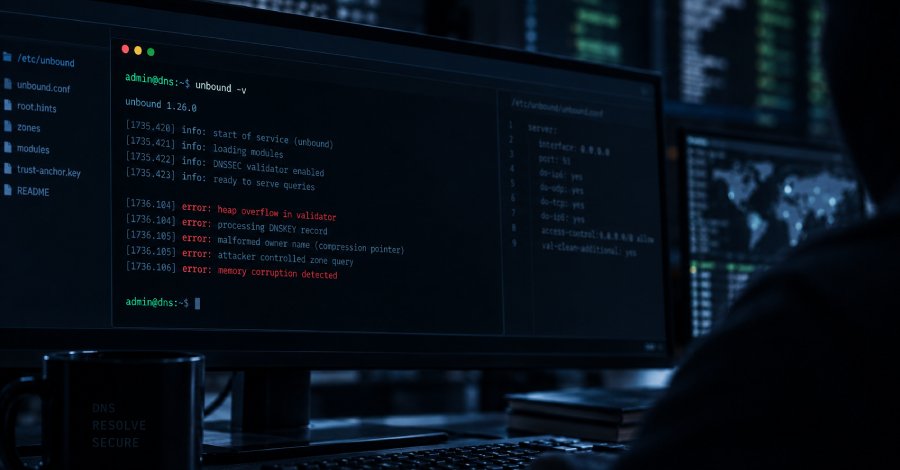
NLnet Labs announced a critical security vulnerability in the Unbound DNS resolver on September 18, 2026. The flaw affects all versions prior to 1.26.1 and allows attackers to gain control over a malicious DNS zone. By sending targeted requests to a vulnerable resolver, a heap overflow can be triggered, leading to remote code execution (RCE). The vulnerability is registered under the CVE number CVE-2026-81642.
According to the advisory from NLnet Labs, attackers could potentially gain full control over the affected system through this vulnerability. The discovery of this flaw poses a significant risk to all users employing the Unbound DNS resolver. Unbound is a widely used DNS resolver found in many network infrastructures. The software is often used in conjunction with other security solutions to process and validate DNS queries. Therefore, the vulnerability could have far-reaching implications for network security, especially in enterprise environments.
The new version 1.26.1 was released on the same day to address the security vulnerability. Users are strongly urged to upgrade to this version to protect themselves from potential attacks. The update also includes additional enhancements and bug fixes that improve the stability and security of the resolver. The vulnerability was discovered by an external security expert and reported to NLnet Labs. The company's swift response to the discovery underscores the importance of proactive security measures in software development.
The release of the advisory and the update comes at a critical time as cyberattacks on DNS infrastructures are on the rise. The impact of the vulnerability could be significant, particularly for organizations relying on Unbound for their DNS services. By exploiting the flaw, attackers could not only steal data but also compromise systems and destabilize networks. This situation further emphasizes the necessity of timely implementation of security updates. NLnet Labs recommends that all users promptly review their systems and perform the update to version 1.26.1.
The organization has also provided additional resources to assist users in implementing the update. This includes guidelines for securely configuring the resolver and checking for potential compromises. The discovery of CVE-2026-81642 is not the first security vulnerability found in DNS software. In the past, there have been several similar incidents that highlight the need for continuous monitoring and improvement of security practices in software development. The community is encouraged to report security vulnerabilities and contribute to the enhancement of the software.
The vulnerability affects not only Unbound but also raises questions about the overall security of DNS resolvers. Experts warn that many organizations may not be adequately prepared for such threats. Implementing security standards and regular updates is crucial to ensuring the integrity of networks. NLnet Labs has announced that they will continue to work on improving the security of their products.
The organization plans to conduct regular security reviews in the future and keep the community informed about new developments. The relevance of security updates is becoming increasingly important in today's digital landscape. The vulnerability CVE-2026-81642 could potentially affect thousands of systems worldwide, as Unbound is used in many different environments. Users should be aware of the risks and ensure that their systems are up to date to protect against potential attacks.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!