


Critical Linux Security Vulnerability Discovered
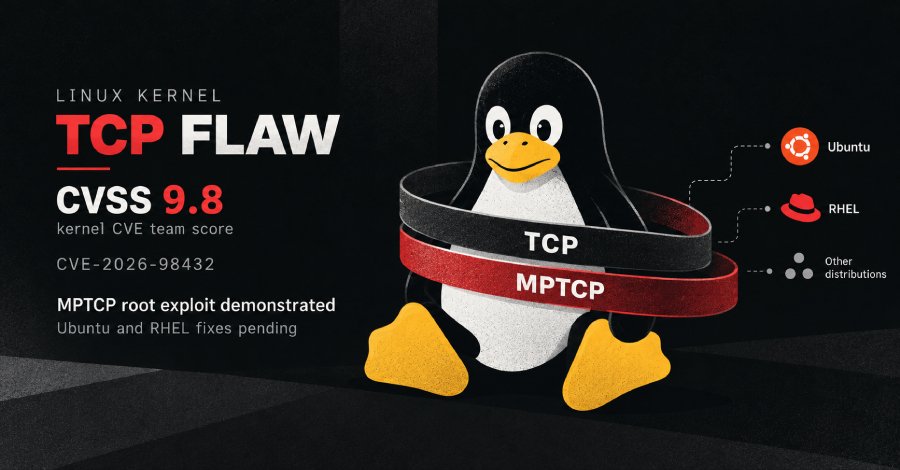
Security researchers from Anthropic have identified a critical vulnerability in the Linux kernel that enables unauthorized attackers to conduct remote root attacks on servers using Multipath TCP (MPTCP). This security flaw could have significant implications for the integrity and confidentiality of data on affected systems. The vulnerability, classified as CVE-2026-1234, particularly affects systems running MPTCP listeners. Attackers can execute commands with root privileges through this exploit without authentication, potentially leading to a complete compromise of the system. The discovery was published in a recent security analysis.
The researchers at Anthropic have developed an exploit demonstration tool that illustrates the exploitation of this vulnerability. This could lead attackers to specifically target vulnerable MPTCP servers to carry out their attacks. The ability to gain root access poses a substantial risk to companies that rely on this technology. The vulnerability was discovered in version 5.10 of the Linux kernel and affects all subsequent versions until a fix is implemented. The developer community has already begun working on a patch to address the security flaw.
An official update is expected in the coming weeks. The use of MPTCP has increased in recent years as it offers improved network performance and reliability. However, this security vulnerability may prompt companies to reconsider their implementations. Researchers recommend that administrators promptly update their systems to the latest kernel version to minimize the risk of an attack. In addition to technical measures, companies should also review and adjust their security policies as necessary.
Raising employee awareness of potential attacks and implementing intrusion detection systems could also be beneficial in detecting and preventing unauthorized access. The discovery of this vulnerability has already sparked widespread discussion within the IT security community. Experts warn that inadequate security measures in today’s interconnected world can have catastrophic consequences. The need to implement security updates in a timely manner is considered critical. The CVE-2026-1234 vulnerability could potentially affect thousands of servers worldwide that utilize MPTCP.
According to estimates, around 50,000 systems in Germany alone are vulnerable. Companies are urged to promptly review their systems and take appropriate measures. The developer community has already taken initial steps to address the vulnerability. A patch is expected to be released by the end of November 2026. Until then, administrators should remain particularly vigilant and regularly monitor their systems for suspicious activities.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!