


CISA Warns of Plex2Shell Security Vulnerabilities
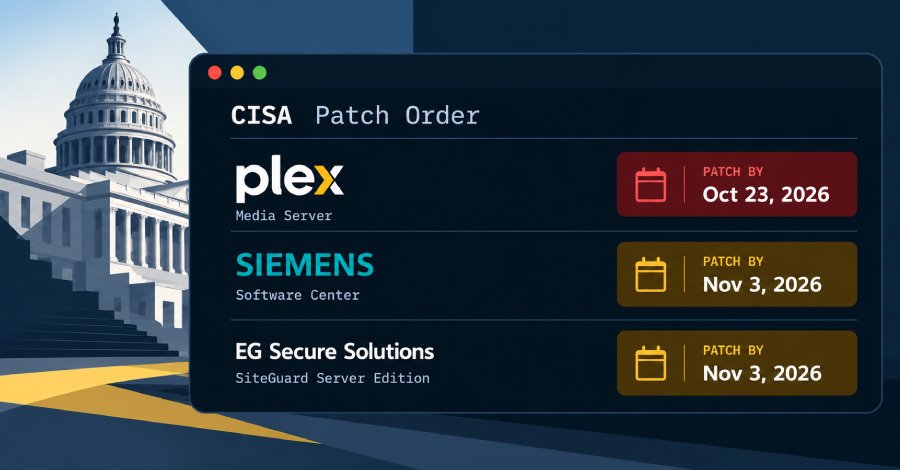
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) announced on Tuesday the addition of four new security vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog. Among these is a group of vulnerabilities known as Plex2Shell, which affect the Plex Media Server. These vulnerabilities allow attackers to conduct Server-Side Request Forgery (SSRF) attacks, potentially leading to data loss. The specific vulnerability identified as CVE-2026-96652 has a CVSS score of 5.3.
This indicates a medium risk that should not be ignored. CISA recommends that all affected organizations promptly implement the necessary patches to protect their systems. In addition to Plex2Shell, CISA has also identified vulnerabilities in Siemens and SiteGuard. These vulnerabilities could also be exploited to gain unauthorized access to systems. CISA has urged the affected companies to review and, if necessary, strengthen their security measures.
The vulnerabilities in Siemens affect several products used in critical infrastructures. The exact number of affected systems is currently unknown; however, the urgency of the patches is high due to the potential impact on public safety. CISA has already collaborated with Siemens to inform the affected customers. SiteGuard, another product with identified vulnerabilities, is frequently used in corporate networks. CISA has pointed out that exploiting these vulnerabilities could lead to significant security risks, especially in environments that rely on the integrity of their data.
CISA has published the vulnerabilities in its KEV catalog to increase visibility and awareness of these threats. Organizations operating the affected systems should follow CISA guidelines and ensure that all necessary updates are carried out promptly. Responding to these security alerts is crucial to preventing potential attacks. CISA has emphasized that timely implementation of security updates is one of the most effective methods to avoid cyberattacks. The agency plans to provide further information and resources to assist companies in implementing the required measures.
CISA has issued similar warnings in the past, leading to an improved security posture in many organizations. The agency has determined that proactive identification and remediation of vulnerabilities are critical for protecting critical infrastructures. The release of these vulnerabilities occurs in a context where cyberattacks are becoming increasingly complex and targeted. According to CISA, the vulnerability CVE-2026-96652 affects a wide range of Plex Media Server installations worldwide. The exact number of affected systems has not yet been determined; however, it is estimated that millions of users could be at risk.
CISA has urged users to take immediate action to secure their systems. CISA will continue to monitor developments regarding these vulnerabilities and provide regular updates. The agency has announced that it will release additional information on the necessary patches and security measures in the coming weeks. The vulnerabilities were added to the KEV catalog on October 21, 2026, underscoring the urgency of the situation. Organizations are urged to review their systems immediately and take the necessary steps to remediate the vulnerabilities.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!