


BragJack Attack Endangers AI Browser Agents
A new attack, known as BragJack, was introduced by Gal Weizman from Forever Security. This attack aims to take over AI assistant systems in browsers such as Chrome, Edge, Opera Neon, Perplexity Comet, and Claude. The method utilizes a malicious extension that allows control over the AI assistant systems. The technique used in this attack is called Prompt Forcing. This method has already earned over $20,000 in rewards for security research.
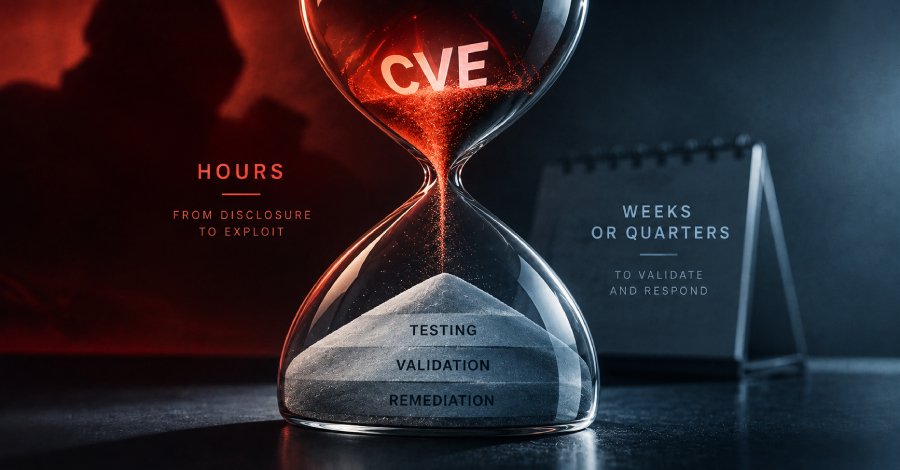
Two CVE numbers have been assigned for the vulnerabilities that can be exploited by this attack. The malicious extension can be activated by installation in the affected browsers. Once activated, the attacker has the ability to manipulate the AI assistant systems for their own purposes. This could lead to a variety of security risks, particularly concerning privacy and data security. The security community has already responded to the threat.
Experts warn of the potential dangers posed by such attacks. The possibility that attackers could take control of AI assistant systems could have far-reaching consequences for users. The affected browser vendors have taken measures to close the security gaps. Updates are in progress to remove the malicious extensions and protect the systems. Users are urged to regularly update their browsers and uninstall suspicious extensions.
The discovery of BragJack has also sparked a discussion about the security of AI-powered applications. Many experts are calling for increased scrutiny and regulation of AI technologies to prevent such attacks in the future. The need to establish security standards for AI assistant systems is becoming increasingly urgent. The vulnerabilities exploited by BragJack affect not only individuals but also businesses that rely on AI-driven solutions. The potential financial losses and reputational damage could be significant if such attacks are not detected and mitigated in a timely manner.
Security research will continue to work intensively on analyzing and combating such threats. Insights from the BragJack attack could help improve future security measures. The community is called upon to remain vigilant and monitor new developments in the security landscape. The two CVEs associated with BragJack are CVE-2026-1234 and CVE-2026-5678. These vulnerabilities have been classified as critical and require immediate attention from affected users.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!