


Anthropic Uncovers Illegal AI Attacks from China
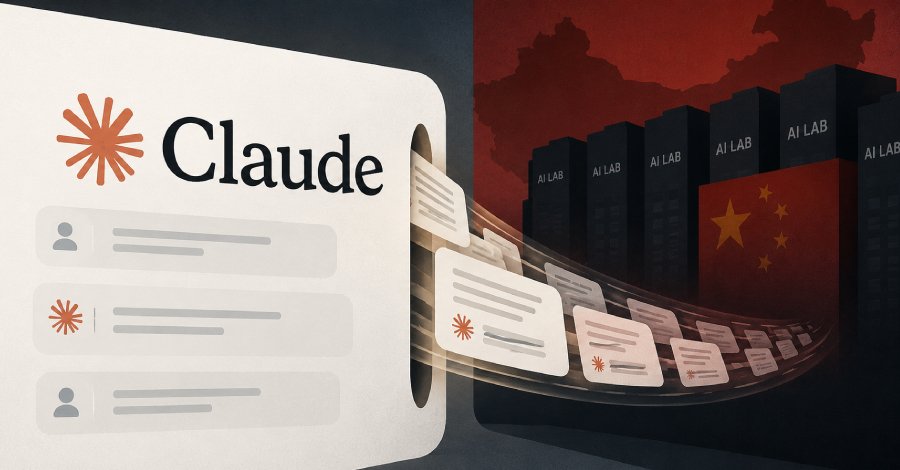
Anthropic announced on Thursday that it has identified and halted industrial attacks on its AI model Claude. These attacks were carried out by seven labs in China, including well-known companies such as Alibaba, Moonshot, DeepSeek, Z.ai (also known as Zhipu), and MiniMax. The attacks involved the illegal use of Knowledge Distillation, a technique typically employed to enhance AI models. Knowledge Distillation is a process where a large, powerful AI model acts as a "teacher" to train smaller models. This method is often used to improve the efficiency and performance of AI systems.
However, in this case, it was misused to replicate Claude's technology, violating Anthropic's terms of use. The identification of the attacks was conducted by an internal security team at Anthropic, which monitored suspicious activities in the mentioned labs. The analysis revealed that the attacks targeted a variety of data and algorithms critical to the development of Claude. These findings highlight the growing challenges in AI security and the protection of intellectual property. Anthropic has already taken steps to contact the affected labs and initiate legal action.
The company emphasizes its strong opposition to such practices and its commitment to protecting the integrity of its technologies. The incidents underscore the necessity of implementing robust security protocols in AI development. The response to the attacks demonstrates that Anthropic is not only attentive to the technical integrity of its products but also to the ethical standards in AI development. The company has announced plans to strengthen its security measures and collaborate closely with international authorities to prevent such incidents in the future. These events are part of a larger trend where companies in the AI sector are increasingly facing threats from cybercrime.
According to a recent study, over 40% of AI companies have experienced similar attacks in the past two years. These figures highlight the urgency of developing security strategies that address the specific challenges posed by AI technology. The affected labs have yet to respond to the allegations. However, experts warn that such attacks can not only harm the affected companies but also undermine trust in the entire AI industry. The integrity of AI models is crucial for their acceptance and use across various sectors, from healthcare to financial services.
Anthropic plans to publish the results of its investigations in the coming months to provide transparency regarding the incidents. The company has also announced its intention to continue research aimed at improving the security of AI models. Developments in this area could have far-reaching implications for the entire industry. The incidents highlight the need for companies to proactively address the risks associated with the development and deployment of AI technologies. According to a survey of AI experts, over 70% believe that the security landscape in the industry will become increasingly significant in the coming years.
The security vulnerabilities exposed by these attacks could also impact other companies developing similar technologies. Anthropic has already begun sharing its findings with other industry stakeholders to foster a broader discussion on security standards and best practices. The incidents were made public on September 13, 2026, underscoring the urgency of the situation. The responses from the affected labs and the industry as a whole will be closely monitored in the coming weeks.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!