


Access Key Theft Leads to Security Incident at Anthropic
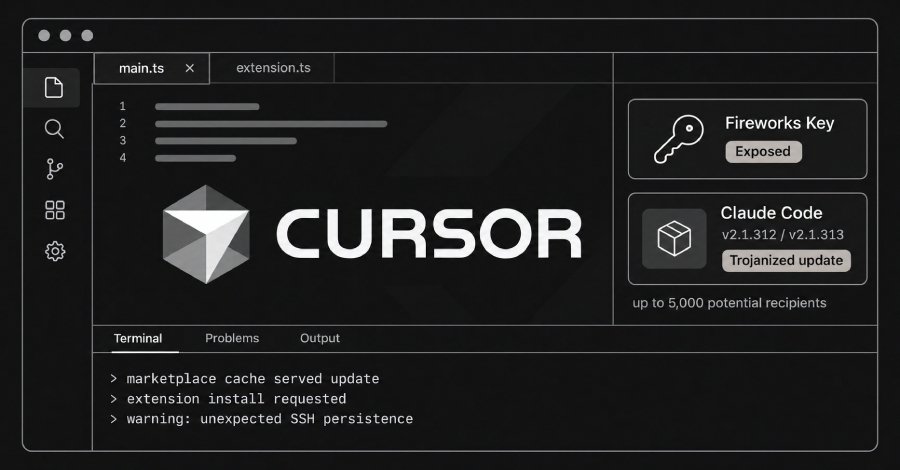
The compromise of Anthropic's official Claude Code extension on the Cursor marketplace was caused by the theft of an access key. This key was exposed as a result of a security incident at Fireworks AI. Cursor announced on Friday that an attacker obtained the access key, originally issued for Fireworks, and used it to copy data from a read-only source. The incident raises questions about the security of access keys and their management. Cursor stated that the key was exposed by Fireworks, enabling the attackers to access sensitive data.
The exact nature of the data that was copied was not specified by Cursor; however, the potential impact on Claude Code users is significant. Fireworks AI has not publicly commented on the incident so far. The vulnerability that led to the exposure of the access key could also affect other services relying on Fireworks AI. Experts warn that such incidents can undermine the trustworthiness of third-party platforms. The Claude Code extension is used by developers to access Anthropic's AI capabilities.
The compromise may force developers to reconsider their projects, especially if they rely on the integrity of the tools they use. Cursor has announced plans to take measures to enhance the security of its platform and prevent similar incidents in the future. The security community has responded to the incident by emphasizing the importance of securely managing access keys. Experts recommend regularly rotating access keys and ensuring they are not stored in publicly accessible repositories. The use of environment variables to store sensitive information is also highlighted as a best practice.
Incidents at Fireworks AI and Cursor are not the first of their kind in the tech industry. In recent years, there have been several similar security incidents caused by the exposure of access keys or other sensitive information. These incidents have led to an increased focus on security protocols and policies within companies. The industry is closely monitoring Anthropic's response to the incident. The developer community expects clear guidelines and actions to improve the security of the Claude Code extension.
A spokesperson for Cursor stated that they are working with Anthropic to assess the impact of the incident and take necessary steps to restore trust. The vulnerability that led to the exposure of the access key could have far-reaching consequences for Claude Code users. Cursor has announced that they will inform all affected users to ensure that they can take appropriate measures. However, the exact number of affected users has not been disclosed. The incidents underscore the need for companies to implement robust security measures and regularly review them.
The vulnerability at Fireworks AI could serve as a wake-up call for other companies to review and improve their own security protocols. According to a recent survey, 78% of IT security experts believe that companies should invest more in training for the secure handling of access keys. Cursor plans to enhance security measures by the end of 2026 to prevent similar incidents in the future. The exact details of the new security protocols will be released in the coming weeks.
💬 Comentarii (0)
Inca nu exista comentarii. Fii primul!